WordPress Cookie Notice in 2026: 7 Live Checks Before You Enable a Plugin
The real value in wordpress cookie notice shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for wordpress cookie notice is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
A wordpress cookie notice is part of a runtime control system. It affects what scripts load, what third parties receive data, how your privacy page stays accurate, and whether visitors can actually refuse or revisit tracking choices.
This is why the official guidance still matters here. The UK’s ICO says services using cookies and similar technologies must provide “clear and comprehensive information”, “must not pre-enable” non-exempt technologies, and should make withdrawal as easy as acceptance. California’s Department of Justice says a notice at collection must link to the privacy policy so a person can get a “fuller description” of privacy practices and rights. WordPress says its built-in privacy tools can help generate starter text, but it remains your responsibility to “keep your policy current and accurate.”
If you want the closest companion reads first, start with these guides to WordPress cookie consent, website privacy checker, and WordPress privacy policy generator. This page stays narrower. It is about what a wordpress cookie notice must actually do before you trust a plugin toggle and move on.
If your team is trying to get wordpress cookie notice under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team needs help turning the notice into a working control layer, DataShyre can help with consent management, data mapping, and DSR automation. The visible banner is usually the easy part. The harder part is keeping forms, embeds, tags, and rights workflows aligned with what the notice promises.
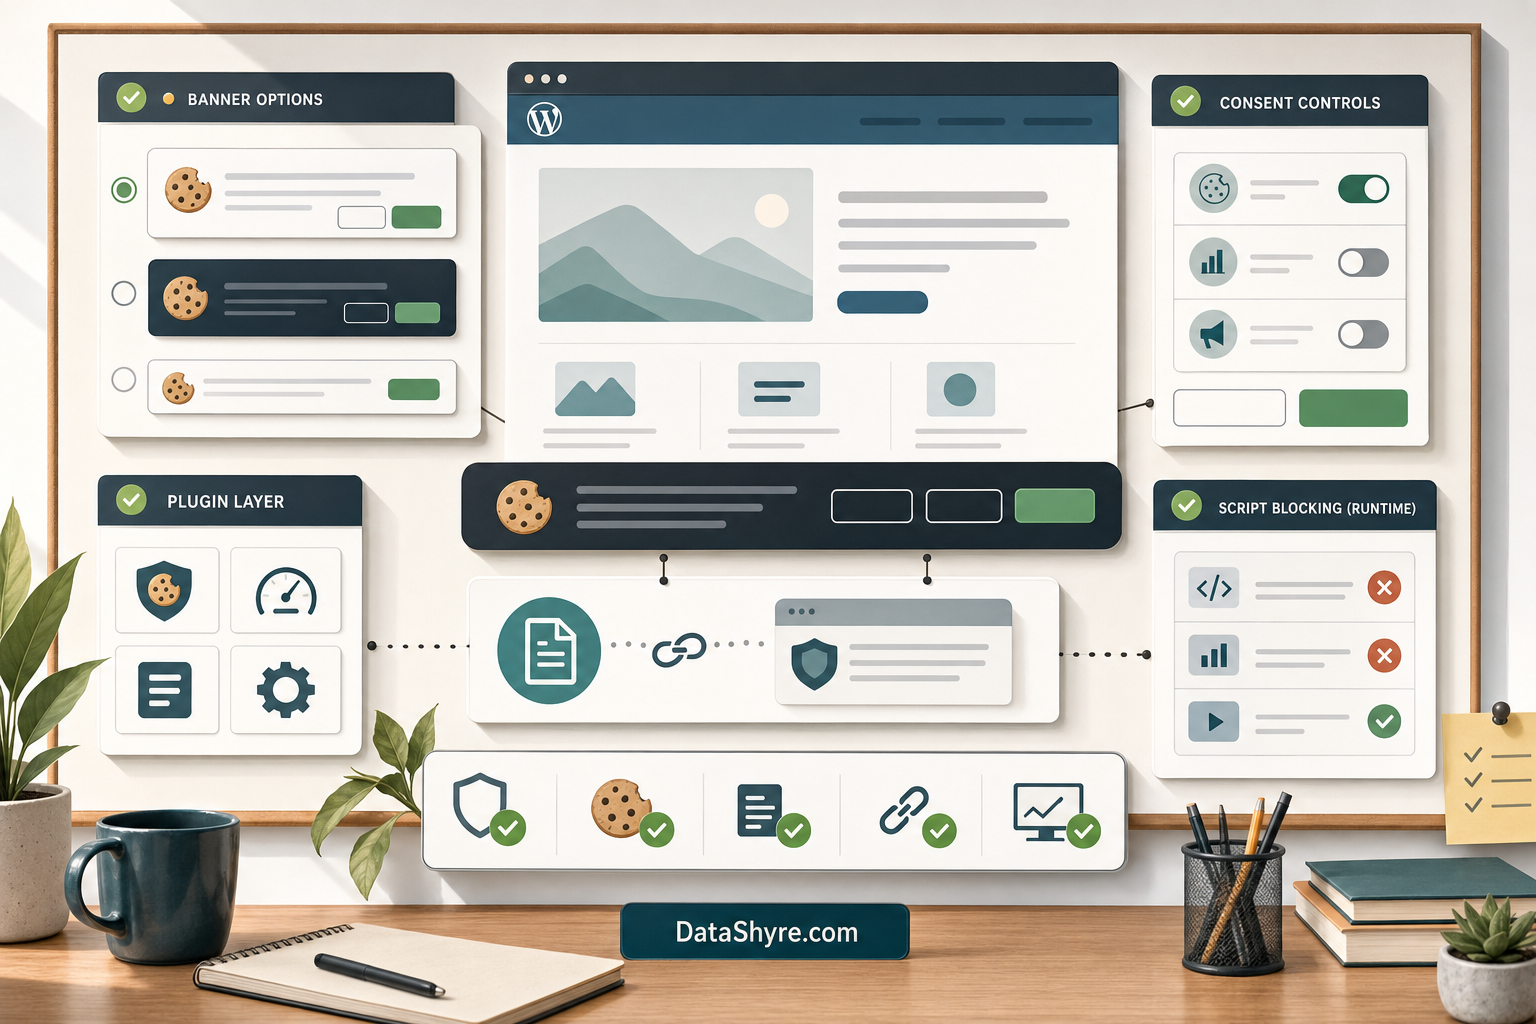
1. Treat the notice as a control surface, not just a message
The first wordpress cookie notice mistake is evaluating the plugin like it only changes text and button colors.
In real deployments, the notice sits in front of:
- analytics tags;
- advertising pixels;
- chat widgets;
- video or map embeds;
- personalization tools;
- consent logs and preference updates.
This is why a banner can look polished while still failing in production.
If your site serves visitors in jurisdictions where prior consent is required for non-essential technologies, the real question is not does the banner appear.
It is what loads before the visitor chooses.
2. Test what the plugin blocks before consent, not what the settings screen claims
The ICO’s current storage-and-access guidance is unusually direct here. It says organizations must not pre-enable non-exempt storage and access technologies and must explain them in a way people can understand.
That means a wordpress cookie notice review should always include a runtime test:
- open a clean browser session;
- load the site before interacting with the banner;
- inspect which scripts, cookies, local storage items, pixels, or embedded calls appear;
- reject non-essential choices;
- verify the same technologies stay blocked after rejection.
This matters even more on WordPress because page builders, optimization plugins, tag managers, and embed modules can inject code before the notice logic catches up.
A plugin that says GDPR ready is not proof that your actual site is blocking correctly.
3. Compare the notice against the real plugin stack and privacy-policy text
WordPress’s plugin privacy guidance says every plugin that collects, uses, or stores user data, or passes it to a third party, should add suggested text for the site’s privacy policy.
That is a useful review rule for any wordpress cookie notice setup.
Before you publish the notice, compare it against the live stack:
- analytics and tag-manager plugins;
- form builders and CRM connectors;
- video, map, chat, and social embeds;
- advertising or retargeting tools;
- performance, A/B testing, or personalization services.
If the notice says we use cookies but the privacy page never explains which tools receive data and why, the disclosure layer is already drifting.
WordPress can help assemble starter text, but it does not remove the admin’s obligation to keep the page accurate as plugins change.
4. Make the reject path and revisit path as obvious as the accept path
This is where many wordpress cookie notice plugins still underperform.
The banner often ships with:
- a bright accept button;
- a weaker secondary path for refusal;
- a buried settings link;
- no persistent way to revisit the choice later.
The ICO’s guidance says it should be as easy to withdraw consent as it is to give it. That is a practical UX test, not a decorative principle.
So when you review a wordpress cookie notice, ask:
- can a visitor reject without extra friction;
- is the choice stored consistently across pages;
- is there a visible footer link, icon, or settings entry to reopen preferences;
- does reopening preferences actually stop later non-essential loading when consent is withdrawn.
If the answer to any of those is no, the notice is not finished.
5. Check the California path too, especially if you use ad-tech or cross-context sharing
Not every wordpress cookie notice issue is an EU-only issue.
California’s DOJ says the notice at collection must link to the privacy policy for a fuller description of privacy practices and rights. The CPPA’s FAQ says businesses that sell or share personal information must honor qualifying opt-out preference signals such as Global Privacy Control, and their privacy policy must explain how people can exercise those rights.
So if your WordPress site uses ad-tech, retargeting, or other sharing flows, your wordpress cookie notice review should include:
- whether the privacy policy linked from the site clearly explains the rights path;
- whether Global Privacy Control is honored where required;
- whether your site can show the consumer the status of an opt-out request where that rule applies;
- whether the notice and the linked privacy page describe the same real behavior.
A cookie plugin can help with interface behavior, but it does not automatically solve downstream California opt-out handling.
6. Test the pages editors actually change: popups, landing pages, embeds, and builders
Many wordpress cookie notice failures do not happen on the homepage.
They happen on:
- campaign landing pages built in a page builder;
- blog posts with embedded video or maps;
- popup forms added by marketing plugins;
- region-specific pages with custom scripts;
- checkout or scheduling flows with extra vendor code.
This is where WordPress’s own privacy documentation is helpful in a slightly uncomfortable way. It explicitly warns that the platform’s helper may not detect everything collected through third-party services, such as analytics providers, newsletter tools, ad partners, or embedded media.
So a serious wordpress cookie notice test runs on the templates editors touch most, not only on one clean demo page.
If your stack includes builder modules, external embeds, or consent rules that vary by market, that is also where DataShyre implementation help can save time. The governance problem is usually in the edge pages, not the pretty homepage demo.
7. Recheck the notice whenever the stack changes
The most expensive wordpress cookie notice assumption is that you only need to configure it once.
WordPress updates. Plugins update. Marketing adds a new pixel. A builder template adds a video embed. A new form connects to a different CRM.
And suddenly the old notice no longer matches the live page.
This is why a wordpress cookie notice should be part of release governance:
- recheck after new plugins or major plugin updates;
- recheck after new embeds or campaign tools go live;
- recheck after privacy-page edits or rights-flow changes;
- recheck after regional targeting rules change.
The banner should evolve with the stack, not trail behind it.
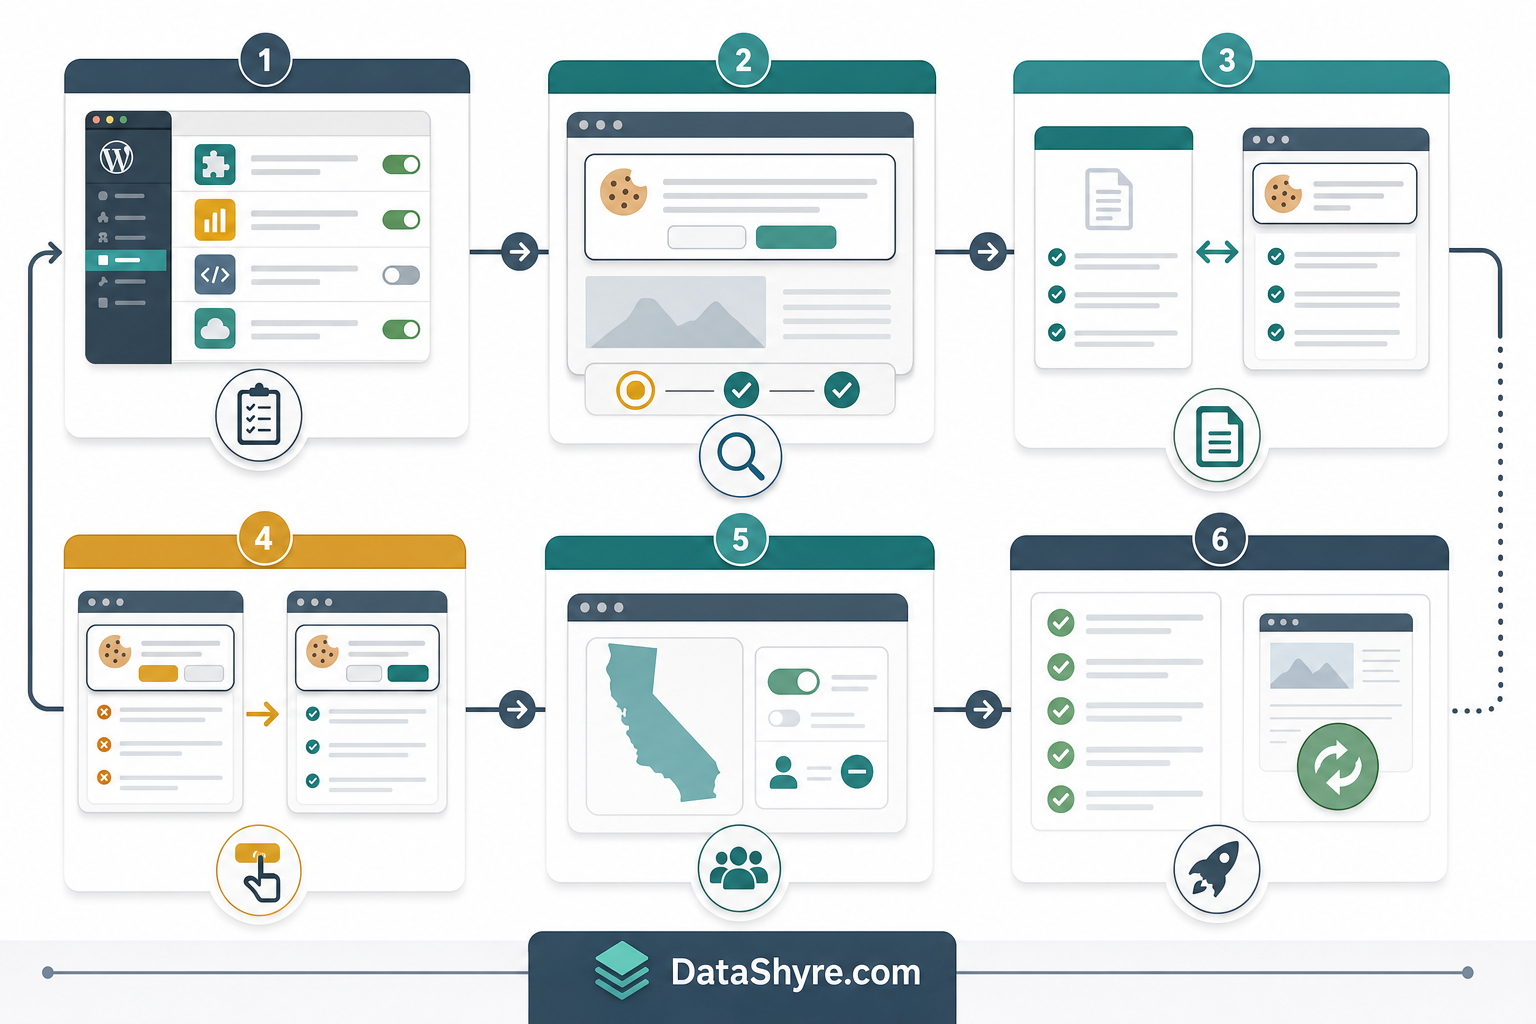
A practical 7-step review for this week
If I were auditing a wordpress cookie notice today, I would use this order:
- inventory all plugins, embeds, tags, and pages that can set or trigger storage and access technologies;
- test what loads before any consent action;
- test reject, accept, and withdraw flows on real pages;
- compare the banner language against the privacy page and plugin disclosures;
- check California opt-out and GPC handling if ad-tech or sharing is involved;
- retest landing pages, builders, popups, and embedded-media pages;
- add the notice review to release and plugin-change checklists.
That order catches more real failures than rewriting the banner copy first.
FAQ
Is a WordPress cookie notice the same as consent management?
No. The notice is only one visible layer. The real compliance question is whether the site blocks, logs, respects, and updates non-essential technologies correctly.
Can I rely on a plugin’s default settings?
Usually not. Default settings often need review for blocking behavior, category mapping, linked disclosures, and revisit controls.
Does WordPress automatically keep the privacy page accurate?
No. WordPress provides helper tools and participating plugins can contribute suggested text, but WordPress says it is still the administrator’s responsibility to keep the policy current and accurate.
Bottom line
A wordpress cookie notice in 2026 is not a cosmetic banner decision.
It is a live control point between your visitors and the parts of the site that store, access, share, or activate tracking technology.
If the plugin blocks correctly, links to an honest privacy page, respects rejection and withdrawal, and stays aligned with real runtime behavior, the notice is useful.
The fastest way to judge wordpress cookie notice is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.