Sample Website Privacy Policy in 2026: 7 Checks Before You Copy One
The real value in sample website privacy policy shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for sample website privacy policy is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
A useful sample website privacy policy is not finished copy. It is a starting structure that helps you turn real collection points, real vendors, real cookies, and real rights workflows into something a person can read and compare against reality.
That distinction still matters. California’s official CCPA guidance says consumers should get a notice at collection at or before the point where personal information is collected, and that notice must link to the business’s privacy policy for fuller detail. The GDPR’s official text still requires the information in Articles 13 and 14 to be provided in a concise, transparent, intelligible, and easily accessible form, using clear and plain language. WordPress also still reminds site owners that plugin and theme suggestions are only a starting point, and that it remains the site’s responsibility to keep the policy current and accurate.
If you want nearby context first, start with these guides to privacy policy template, website privacy policy template, and website privacy checker. This page stays narrower. It is the sample website privacy policy review I would use this week before copying one into a real website.
If your team is trying to get sample website privacy policy under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team is trying to move from sample text to a privacy page that actually matches the systems behind it, DataShyre can help with data mapping, consent management, and DSR automation. If you want the short version, book a demo.
1. Treat the sample website privacy policy as a scaffold, not the source of truth
The biggest sample website privacy policy mistake happens before anyone edits the first sentence.
Teams begin with the sample instead of the live site.
That usually means the published page is less specific than the actual collection behavior already running through:
- contact or demo-request forms;
- newsletter or lead-capture forms;
- login, account, or checkout flows;
- analytics and advertising tags;
- chat, scheduling, or support embeds;
- video, maps, or social widgets; and
- CRM, support, or marketing automations behind the scenes.
The ICO’s drafting guidance still starts in the right place: know what personal data you have and what you do with it before drafting privacy information. That is also the only sensible way to use a sample website privacy policy. First map the real collection points, then use the sample to structure the explanation.
Before copying any sample into production, build a current inventory of:
- what categories of personal data the site collects;
- where each category is collected;
- why it is used;
- which vendors or internal teams receive it;
- how long it is retained or how the period is set; and
- what user controls can change or stop the downstream use.
The sample is just the shell. The inventory is the real input.
2. Make the sample answer the disclosure questions regulators still care about
A good sample website privacy policy should help a visitor answer normal questions without decoding legal wallpaper.
California’s Department of Justice says a privacy policy gives a broad picture of the business’s collection, use, sharing, and sale practices and must explain consumers’ rights and how to exercise them. Articles 13 and 14 of the GDPR still point in the same practical direction, even if the framework is different: people should be told who is processing the data, why, on what basis where applicable, who receives it, how long it is kept, and what rights they have.
So a workable sample website privacy policy usually needs clean sections for:
- who operates the website and how to contact them;
- what categories of personal data are collected;
- where the data comes from;
- why each category is used;
- the legal basis where GDPR or UK GDPR applies;
- who receives the data or what categories of recipients receive it;
- how long data is kept or how retention is decided;
- what rights apply; and
- how a person can use those rights in practice.
If your sample does not force the writer to fill those gaps concretely, it is too vague to be useful in 2026.
3. Connect the full policy page to the moments where data is actually collected
One reason a sample website privacy policy fails is that it gets published as a footer page while the forms, account screens, and app flows do their own thing.
California’s official guidance says notice at collection must appear at or before collection and link to the privacy policy. In real deployments, that usually means you need both:
- a fuller privacy-policy page; and
- shorter just-in-time notices near forms, checkout, registration, or other collection points.
The ICO’s guidance pushes the same operational idea from the transparency side: adapt the information to the context and make it easy to access. So when you copy a sample website privacy policy, do not just ask whether the page exists. Ask whether the actual collection screen gives the person enough context when they are about to type.
That means checking whether your sample is reflected in:
- form disclosures;
- checkbox labels and preference text;
- app settings or account menus;
- cookie or preference-center links; and
- download, signup, or onboarding screens.
A polished footer page cannot rescue a confusing collection flow.
4. Give cookies, pixels, and embedded tools their own honest section
This is one of the first places a copied sample website privacy policy falls apart.
Many samples still hide tracking under bland phrases like usage data or technical information.
That is rarely enough if the real website is running analytics, ad pixels, session-replay tools, video embeds, map widgets, or third-party chat.
WordPress’s plugin privacy guidance is still a useful reminder here because it explicitly expects plugins that collect, use, store, or pass user data to third parties to suggest privacy-policy text. Those prompts exist because a lot of websites collect more than the visible forms suggest.
So a stronger sample website privacy policy should explain:
- what cookies or similar technologies are used;
- whether they are necessary, analytics, advertising, embedded-media, or support tools;
- whether third parties receive information through them;
- how banner or preference-center choices affect them; and
- where users can review or change those settings later.
If this part is the weak spot, our cookie policy and this website uses cookies guides are the better next reads because they stay closer to runtime tracking behavior.
5. Make the rights section usable, not decorative
Listing rights is easy. Making them work is where the risk starts.
California’s official pages still point consumers to the privacy policy to understand their rights and how to exercise them. The rights picture can include knowing, deleting, correcting, opting out of sale or sharing, limiting certain sensitive-personal-information uses, and non-discrimination where the law applies. The CPPA also says businesses subject to the CCPA must post the privacy policy through a conspicuous link using the word privacy on the homepage and other webpages.
That means a practical sample website privacy policy should explain:
- which rights apply in the relevant jurisdictions;
- how a person submits a request;
- whether there is an account route and a public route;
- how opt-out or preference controls appear on the site or app;
- whether browser-based signals such as Global Privacy Control are honored where applicable; and
- where a person can go if the first route fails.
If a sample merely lists the rights without connecting them to working paths, it is not helping the reader or the business very much.
6. Check the sample against vendors, plugins, and generated text before you publish
A sample website privacy policy becomes risky when the sample describes a simpler business than the one you actually operate.
That mismatch usually appears after:
- a new CRM or support tool is connected;
- a new analytics or ad-tech destination is added;
- a scheduling or chat widget goes live;
- a plugin changes what data it collects or shares; or
- a generator or WordPress helper creates starter text that nobody audits.
WordPress’s privacy settings guidance is blunt about this: the platform can help create a page and offer suggestions, but it is still your responsibility to use those resources correctly and keep the information current and accurate.
So before you approve a sample website privacy policy, compare it against:
- your tag manager and analytics destinations;
- plugin and theme privacy suggestions;
- CRM, support, and scheduling tools;
- payment, fraud, or identity vendors;
- embedded third-party media or widgets; and
- any advertising or affiliate tooling still active in production.
If you are doing this review because your policy page has drifted away from the systems behind it, DataShyre can help close that gap with data mapping and implementation support for consent operations.
7. Review the sample on every meaningful release, not just once a year
California’s consumer guidance says a business’s privacy policy should be updated at least once a year.
That is a floor, not a strong operating model.
The ICO’s guidance also says privacy information should stay under review and be updated before you start using personal data for a new purpose. That is the better way to think about a sample website privacy policy after it goes live.
So the safer review trigger is not calendar says twelve months passed.
It is:
- a new form or onboarding path launches;
- a new cookie, SDK, pixel, or embed is added;
- a new vendor begins receiving data;
- a new region or rights workflow is introduced;
- a retention rule changes; or
- the site’s consent, opt-out, or settings flow changes.
That is how a sample becomes a maintained privacy page instead of stale filler in the footer.
A practical 7-step review for this week
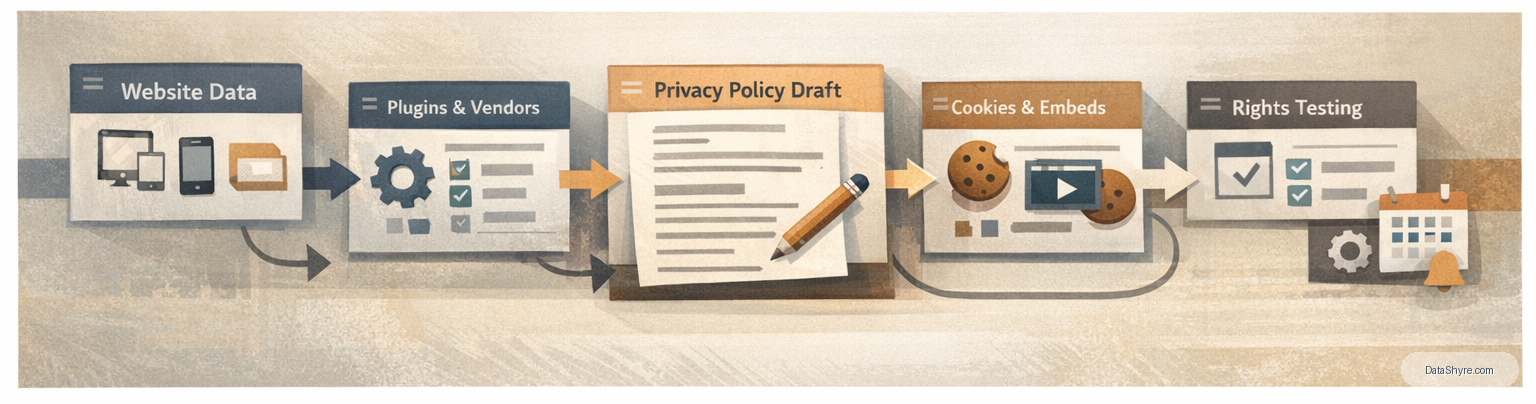
If you were reviewing a sample website privacy policy this week, use this order:
- map the real collection points and vendors first;
- fill the core sections for collection, purposes, recipients, retention, rights, and contact paths;
- add a real tracking section for cookies, pixels, and embedded tools;
- compare the draft against live forms, plugins, tags, and app screens;
- test the rights and opt-out paths the page describes;
- make sure collection-point notices and settings menus link cleanly into the fuller policy; and
- tie future stack changes to a required privacy-policy review.
That order gives you a much better sample website privacy policy outcome than polishing paragraphs before anyone has checked the site.
FAQ
Can I copy a sample website privacy policy and just change the company name?
You can use a sample as a starting structure, but you should not treat it as finished copy. The page still has to match your real forms, tracking, vendors, retention, and rights workflow.
Is the WordPress privacy page generator enough on its own?
No. WordPress can help create a page and collect suggested text from core, themes, and plugins, but it does not confirm that your live configuration, vendor setup, or collection points are accurately described.
Do I need a separate cookie policy too?
Often yes. A main privacy policy can summarize tracking practices, but a separate cookie policy or consent guide is often the clearer place to explain cookie categories, embedded tools, preference controls, and runtime behavior in more detail.
Bottom line
The best sample website privacy policy in 2026 is not the one that sounds the most legal.
It is the one that matches the site’s real data collection, explains tracking honestly, gives people usable rights paths, and gets reviewed when the stack changes.
If your current page cannot do that, the problem is not the sample.
The fastest way to judge sample website privacy policy is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- California Department of Justice, California Consumer Privacy Act FAQ: https://oag.ca.gov/privacy/ccpa
- California Department of Justice, How to Read a Privacy Policy: https://www.oag.ca.gov/privacy/facts/online-privacy/privacy-policy
- California Privacy Protection Agency, FAQs: https://cppa.ca.gov/faq
- EUR-Lex, Regulation (EU) 2016/679, Articles 12 to 14: https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:32016R0679
- ICO, How should we draft our privacy information?: https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/individual-rights/the-right-to-be-informed/how-should-we-draft-our-privacy-information/
- WordPress.org Developer Handbook, Suggesting text for the site privacy policy: https://developer.wordpress.org/plugins/privacy/suggesting-text-for-the-site-privacy-policy/
- WordPress.org Documentation, Settings Privacy screen: https://wordpress.org/documentation/article/settings-privacy-screen/