Privacy Policy Template for Website in 2026: 7 Checks Before You Publish
The real value in privacy policy template for website shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for privacy policy template for website is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
That difference matters because a website notice is no longer judged only by whether it exists in the footer.
It is judged against what the forms collect, what the cookies and pixels do, which plugins and vendors receive data, and whether the rights path people see on screen really works.
Current official guidance still points in that direction. California’s Department of Justice says a privacy policy should answer basic questions about collection, use, access, and user choices, and says it should be “updated at least once a year.” California’s current CCPA regulations effective January 1, 2026 still require covered businesses to make the privacy policy available online through a conspicuous link using the word privacy and to describe information practices and consumer rights. On the EU and UK side, Article 13 GDPR still requires key notice details such as purposes, legal basis, recipients, transfer information where relevant, retention, and rights. The ICO also says if you want to use personal data for a new purpose, you must update the privacy information before starting that new processing.
If you want nearby context first, start with these guides to privacy policy for website, website privacy checker, and cookie policy. This page stays narrower. It is the privacy policy template for website review I would use this week before publishing one on a real site.
If your team is trying to get privacy policy template for website under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
1. Start with the live website journey, not the generic template
The most common privacy policy template for website mistake is starting from legal-sounding paragraphs before anyone checks the actual site.
That usually creates a page that sounds careful and is still wrong.
For a working privacy policy template for website review, map the live collection points first:
- contact, demo, signup, and checkout forms;
- analytics, advertising, and consent tools;
- chat widgets, embeds, and video players;
- account areas and support flows;
- plugins, apps, and CRM integrations; and
- mobile or app-download paths tied to the website.
That map is the real source material.
The template is only the structure you use to explain it.
2. Make sure the template covers the disclosure blocks websites still need
A useful privacy policy template for website work should let a visitor answer the questions regulators still care about.
California DOJ’s guidance says a privacy policy should explain what personal information is collected, how it is collected, why it is collected, how it is used, who gets access, and what choices users have. The current CCPA framework adds the website-specific expectation that a covered business’s privacy policy be posted online and describe rights and information practices. Article 13 GDPR still adds the notice blocks many U.S.-only templates miss: controller identity, purposes, legal basis, recipients or recipient categories, transfer information where relevant, retention period or criteria, and rights.
So a modern privacy policy template for website usually needs clean sections for:
- who operates the website and how to contact them;
- what categories of personal data the site collects;
- where the data comes from;
- why each category is used;
- the legal basis where GDPR or UK GDPR applies;
- who receives the data or what categories of recipients receive it;
- how long the data is kept or how retention is decided;
- what rights users have; and
- how those users can actually submit a request or change a setting.
If the template cannot support those sections without turning vague, it is too thin for 2026.
3. Turn the rights section into a route a person can really use
This is where a weak privacy policy template for website page becomes risky.
It is easy to list rights in a paragraph.
It is harder to build the path behind them.
California’s current CCPA page still tells consumers to review a business’s privacy policy for instructions on how to exercise their rights, and it still recognizes opt-out requests through a user-enabled Global Privacy Control where applicable. The California Attorney General’s October 29, 2026 settlement with Lyft is a sharp reminder that a privacy policy link is not enough if the actual opt-out route is cumbersome or pushed out of the app or site journey.
That means your privacy policy template for website should explain:
- which rights apply in the relevant jurisdiction;
- how a person submits a request;
- where opt-out or privacy-choice controls appear;
- whether GPC is honored where the law expects it;
- whether account holders have an in-product settings path; and
- what happens after the request is submitted.
The rights section should work like wayfinding, not decoration.
4. Give website tracking, embeds, and plugins their own disclosure layer
This is one of the biggest practical differences between a general template and a privacy policy template for website page.
Website disclosures usually fail on the browser-side tools, not the opening paragraph.
If the site uses cookies, pixels, session tools, embedded video, maps, chat, or social widgets, the policy should say so in plain language and explain how those technologies affect collection, sharing, and user choice.
WordPress’s own plugin handbook is helpful here because it says every plugin that collects, uses, stores, or passes user data to an external source or third party “should add a section of suggested text” to the site privacy policy. That is a direct reminder that the website stack can change the notice faster than the template changes.
So a strong privacy policy template for website should push the writer to confirm:
- what cookies or similar technologies are active;
- whether third-party embeds trigger extra data flows;
- whether plugins contribute their own suggested privacy text;
- how banner or settings choices affect tracking;
- where users can revisit those choices later; and
- whether the live runtime evidence still matches the page.
If you are uncertain about that runtime branch, pair the template review with our website privacy checker workflow before you publish.
5. Reconcile the template with the vendors and promises the website is actually making
A privacy policy template for website page becomes dangerous when it says less than the stack is doing.
That is not only a drafting problem.
It is an accuracy problem.
The FTC’s March 30, 2026 action involving OkCupid and Match said the company shared personal information with an unrelated third party contrary to its privacy promises, and the agency put the lesson plainly: “The FTC enforces the privacy promises that companies make.” That is the cleanest reminder that privacy text can become an enforcement fact pattern.
So before publishing a privacy policy template for website page, compare it against:
- analytics and ad-tech destinations;
- CRM, support, and email systems;
- payment, fraud, and security tools;
- embedded media or social integrations;
- hosting and infrastructure vendors; and
- any affiliate or group-company sharing the business describes elsewhere.
Generic phrases like trusted partners are rarely good enough.
Concrete recipient categories are better because they are easier to test and easier to keep current when the stack changes.
6. Publish the template where website users actually enter the data journey
A privacy policy template for website page can be legally thoughtful and still be badly deployed.
California DOJ points consumers to privacy policies on website homepages and on app landing or download pages. The ICO says privacy information should be easy to access and linked directly. That means the policy should not live only as a buried desktop-footer asset if your real collection starts in a lead form, signup path, consent banner, or logged-in settings screen.
So the deployment review should check whether the template is exposed:
- in the public footer;
- near forms that collect personal data;
- from cookie or privacy-settings entry points;
- on mobile layouts where the site is actually used; and
- on app landing or download paths where the website introduces the app experience.
The best privacy policy template for website outcome is not merely published.
It is reachable at the moment the user needs it.
7. Add change triggers before the next release makes the page false
The biggest long-term problem with a privacy policy template for website is drift.
The ICO’s current drafting guidance says privacy information should be reviewed regularly and updated before starting a new purpose. California DOJ’s annual update reminder is only the floor. The better operating model is to review the page whenever the website changes in a way that changes collection, sharing, choice, or retention.
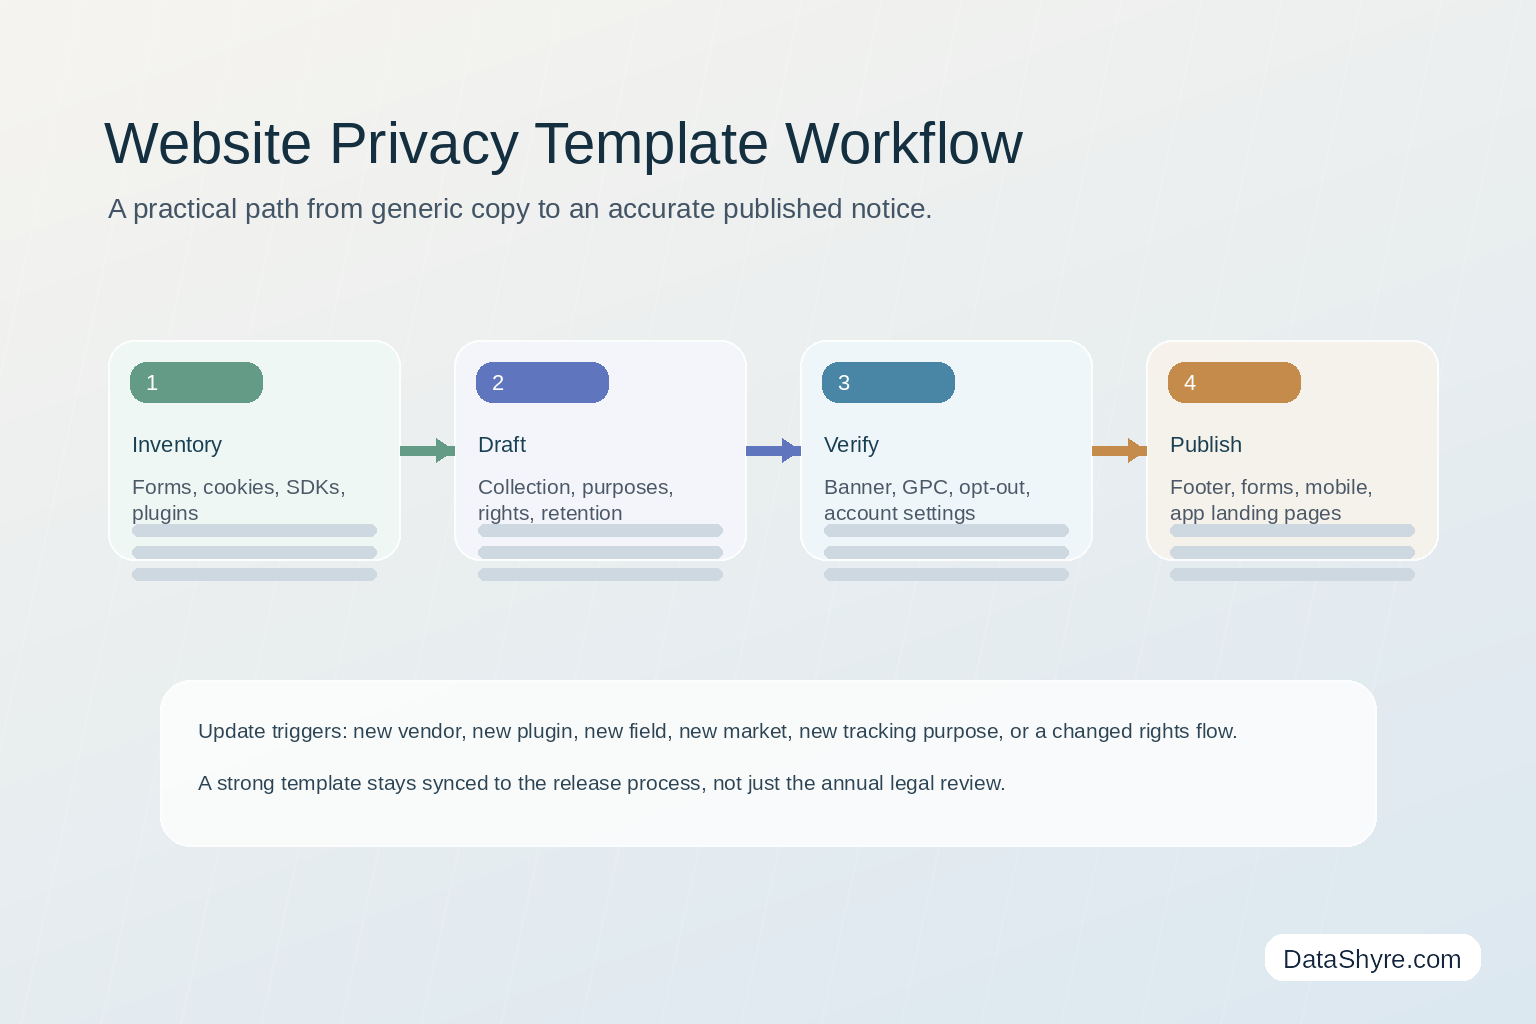
So a useful privacy policy template for website workflow should trigger review when:
- a new plugin, tag, SDK, or embed is added;
- a form starts collecting new fields;
- a new vendor or processor is onboarded;
- a new personalization, analytics, or ad use case launches;
- a new geography or rights flow goes live; or
- the consent or privacy-settings experience changes.
That is how you keep the template connected to the product instead of turning it into a stale legal artifact.
A practical review order for this week
If I were publishing a privacy policy template for website page this week, I would use this order:
- map the live collection and tracking points first;
- fill the core disclosure blocks for collection, purposes, recipients, retention, rights, and contacts;
- isolate the website-specific tracking, embeds, plugins, and settings flows;
- test the rights path and privacy-choice path in the browser;
- compare the page against the real vendor and tag stack;
- publish the notice where the data journey actually starts; and
- tie future site changes to a mandatory policy review.
That sequence usually produces a stronger result than polishing template language before anyone has checked the live site.
FAQ
Is a privacy policy template for website pages enough on its own?
No. It is the disclosure layer, not the whole privacy program. The consent flow, rights operations, vendor controls, and runtime tracking behavior still have to match what the page says.
Can I reuse one website template across several brands?
Only if the underlying collection, tracking, vendors, and rights paths are actually similar. If the stacks differ, one shared template usually becomes too vague to stay accurate.
What is the fastest way to improve a weak template?
Start with the live data journey and remove every sentence you cannot support with a current system, vendor, or workflow. Then add the missing website-specific sections for tracking, plugins, rights, and update triggers.
Bottom line
The best privacy policy template for website pages in 2026 are not the ones with the most clauses.
They are the ones that describe the live website honestly, point users to working rights and settings paths, and get updated before the next release quietly makes the page inaccurate.
If your current template cannot do that, the problem is not only the wording.
The fastest way to judge privacy policy template for website is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- California Department of Justice, How to Read a Privacy Policy: https://oag.ca.gov/node/36676
- California Department of Justice, California Consumer Privacy Act (updated August 28, 2026): https://oag.ca.gov/privacy/ccpa
- California Privacy Protection Agency, CCPA Regulations Effective January 1, 2026 (PDF): https://cppa.ca.gov/regulations/pdf/ccpa_statute_eff_20260101.pdf
- California Attorney General, Lyft settlement announcement dated October 29, 2026: https://www.oag.ca.gov/news/press-releases/privacy-rights-can%E2%80%99t-be-left-rearview-attorney-general-bonta-secures-18-million
- EUR-Lex, Regulation (EU) 2016/679, Article 13: https://eur-lex.europa.eu/legal-content/EN/TXT/?qid=1738102000962&uri=CELEX%3A32016R0679
- ICO, How should we draft our privacy information?: https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/individual-rights/the-right-to-be-informed/how-should-we-draft-our-privacy-information/
- WordPress Developer Resources, Suggesting text for the site privacy policy: https://developer.wordpress.org/plugins/privacy/suggesting-text-for-the-site-privacy-policy/
- FTC, OkCupid/Match case page dated March 30, 2026: https://www.ftc.gov/legal-library/browse/cases-proceedings/okcupidmatch
- FTC, Match and OkCupid action dated March 30, 2026: https://search.ftc.gov/news-events/news/press-releases/2026/03/ftc-takes-action-against-match-okcupid-deceiving-users-sharing-personal-data-third-party