Privacy Policy Generator for Bloggers in 2026: 7 Live Checks Before You Publish
The real value in privacy policy generator for bloggers shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for privacy policy generator for bloggers is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
A useful privacy policy generator for bloggers is a drafting shortcut, not the source of truth. The real job is to make sure the final page matches the live stack behind the blog: newsletter forms, comment systems, analytics, ad tools, affiliate links, embedded media, and the actual path a reader can use to ask privacy questions or exercise rights.
The official sources still point in that direction. California’s Department of Justice says a business privacy policy should be “updated at least once a year.” The California DOJ’s current CCPA page also says a notice at collection must link to the privacy policy for a “fuller description” of privacy practices and rights. GDPR Article 12 still requires privacy information in a concise, transparent, intelligible, and easily accessible form using “clear and plain language.” The ICO still says to “know what personal data you have” before drafting privacy information. The FTC adds the enforcement version of the same idea: if your company makes privacy promises, it must “live up to those claims.”
If you want nearby context first, start with these guides to privacy policy template, online privacy policy, and website privacy policy generator. This page stays narrower. It is the privacy policy generator for bloggers review I would use this week before publishing a privacy page for a live blog.
If your team is trying to get privacy policy generator for bloggers under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team needs help turning a generated draft into something that actually matches the systems behind the blog, DataShyre can help with data mapping, consent management, and DSR automation. The hard part is rarely producing text. It is proving the text still matches the live tools, vendors, and reader-facing controls after the next plugin change or campaign launch.
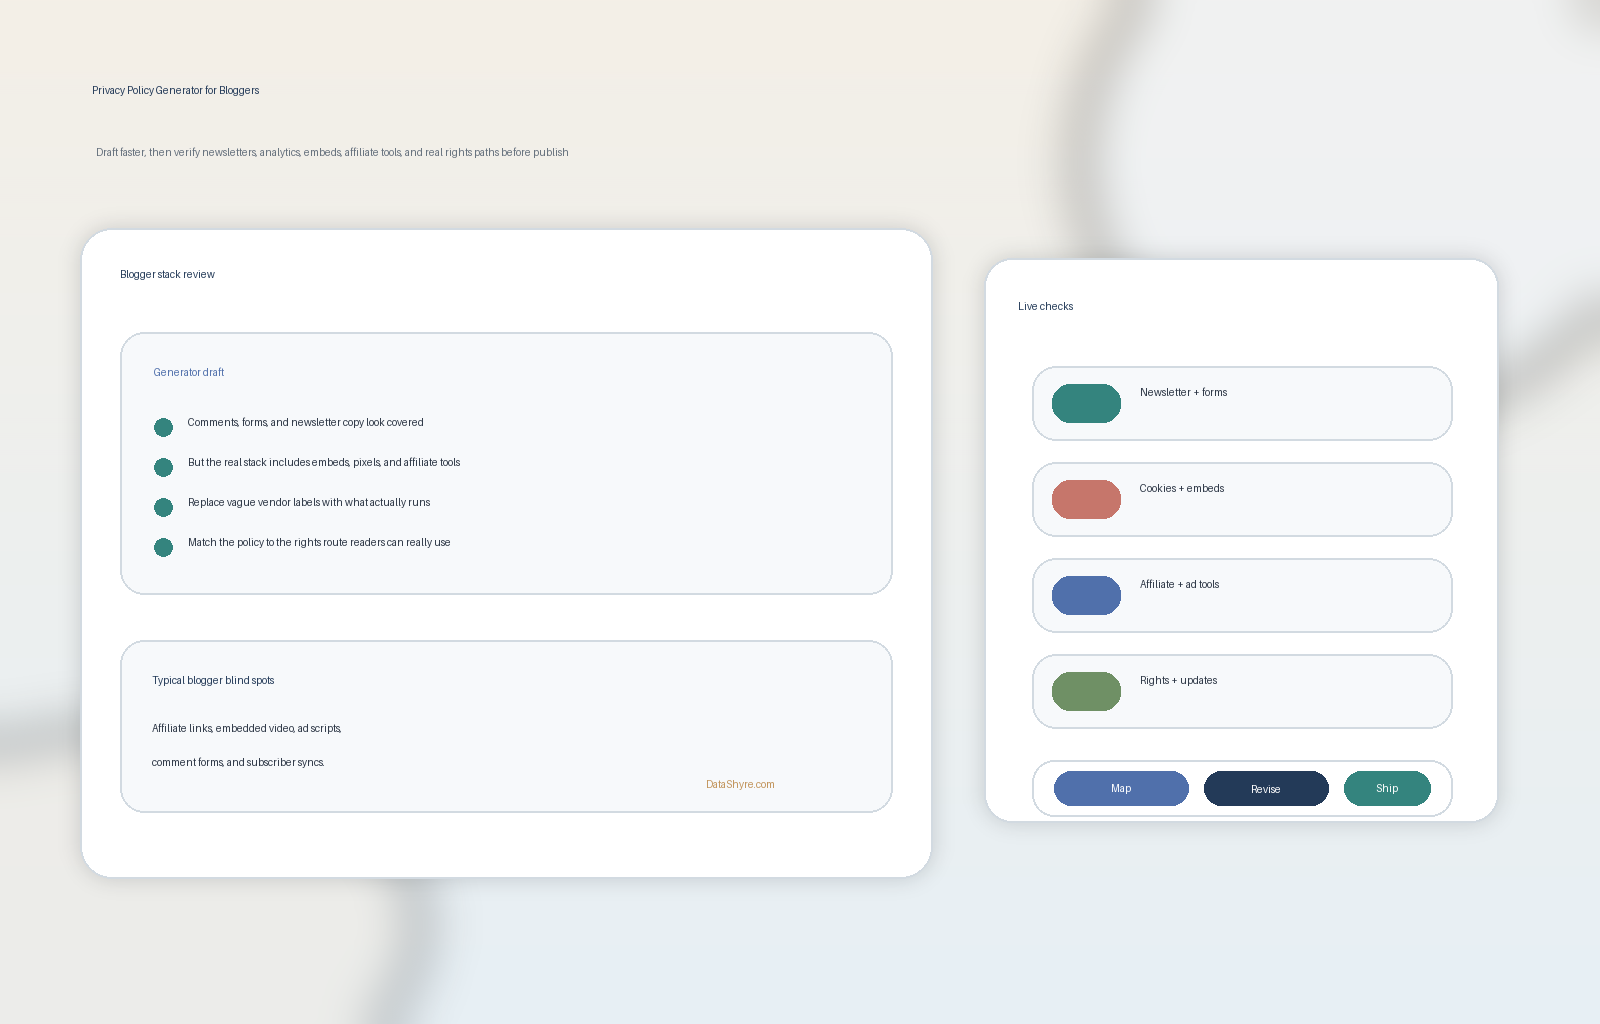
1. Start with the live blog stack, not the generator
The most common privacy policy generator for bloggers mistake happens before anyone edits the first sentence.
The writer trusts the generated page before mapping what the blog actually does.
That is backwards.
The ICO’s drafting guidance still gives the right first step: “know what personal data you have” before drafting privacy information. For a blog, that usually means identifying:
- comment forms and moderation workflows;
- contact, download, demo, or quote-request forms;
- newsletter signup flows and subscriber syncs;
- analytics, pixels, consent tools, and ad scripts;
- embedded video, podcasts, maps, social posts, or scheduling widgets; and
- affiliate, sponsorship, or partner tooling that receives reader data or drops identifiers.
If the inventory is incomplete, the generated policy can still sound polished while missing the real collection story.
2. Treat generated text as starter text only
This is the core point.
A privacy policy generator for bloggers can help structure a page, but it cannot confirm whether the page is true.
That limit shows up clearly in WordPress’s official privacy documentation. WordPress says its Privacy Policy Editing Helper pulls together default texts from core, themes, and participating plugins, but it also says it is still your responsibility to keep the final policy “current and accurate.” The same page adds a warning bloggers should take seriously: many sites use third-party tools, such as newsletter services, analytics providers, ad affiliate partners, or embedded media, that the helper cannot fully detect.
So the safe workflow is not generate and publish.
It is generate, compare the draft against the live stack, then rewrite the sections that do not match reality.
3. Make the policy line up with collection points, not only the footer
This is where a lot of privacy policy generator for bloggers workflows become too passive.
California’s current CCPA guidance says the notice at collection must appear at or before the point where personal information is collected, and that notice must link to the privacy policy for a “fuller description” of the business’s practices and rights.
For a live blog, that means checking more than whether the privacy-policy page exists.
It means checking whether the disclosure is connected to places where readers actually give you data:
- newsletter signup forms;
- lead magnets or download forms;
- contact or support forms;
- comment forms;
- account or member signup pages, if the blog has them; and
- app-download or community links if the blog routes people into a separate product or platform.
The question is not did the generator make a page.
It is does the reader get useful privacy context where the data journey starts.
4. Give cookies, embeds, and affiliate tooling their own honest section
Many weak privacy policy generator for bloggers pages flatten runtime tracking into vague language like usage data or trusted partners.
That is rarely enough for a modern blog.
Even smaller blogs often run a mix of:
- analytics cookies and performance tags;
- ad network or retargeting scripts;
- video or podcast embeds;
- social embeds;
- newsletter or CRM tracking;
- affiliate tools or external commerce widgets.
WordPress’s own privacy guide is useful here because it explicitly says third-party services such as analytics providers, newsletter subscription services, ad affiliate partners, and embedded media may collect data in ways the default helper cannot fully describe.
That means a strong privacy policy generator for bloggers review should explain:
- what cookies or similar technologies are in use;
- whether they are necessary, analytics, advertising, embedded-media, or support-related;
- which outside providers may receive personal data or identifiers through them;
- how consent, opt-out, or preference controls affect those tools; and
- where readers can revisit or change those choices later.
If this branch is the weak spot, our cookie policy and website privacy checker guides are better follow-up reads because they stay closer to runtime behavior.
5. Make the rights section usable, not decorative
Listing rights is easy.
Making them usable is the real test.
California’s official CCPA and CPPA guidance still points people back to the privacy policy to understand their rights and how to exercise them. The CPPA also says businesses subject to the CCPA must post the privacy policy through a link using the word privacy on the homepage and other webpages, and for mobile apps on the download page or in settings.
So a practical privacy policy generator for bloggers review should make sure the page clearly tells readers:
- which rights apply in the relevant jurisdictions;
- how to submit a request or question;
- whether there is an account route and a public route;
- where opt-out or preference controls appear;
- whether browser-based signals such as Global Privacy Control are handled where applicable; and
- what happens after a request is submitted.
If the generated page names the rights but not the working path, the most important part is still missing.
6. Compare the draft against the promises the blog is already making
This is the FTC test.
The FTC says businesses must “live up to those claims.”
That turns a privacy policy generator for bloggers review into an evidence exercise.
Before you publish, compare the draft against:
- the email signup copy on the site;
- any sponsor, partner, or giveaway pages that collect personal data;
- tag-manager or analytics destinations;
- the real cookie banner or preference center;
- published help pages, FAQs, or app settings that talk about privacy; and
- any older privacy statements already indexed by search engines.
If the draft says we only use data to send updates you requested while the live stack also supports remarketing, affiliate measurement, or sponsor integrations, the page is already out of sync.
7. Tie policy review to every meaningful blog-stack change
The biggest long-term privacy policy generator for bloggers weakness is drift.
The page may be accurate on launch day and wrong a week later.
California DOJ says the privacy policy should be “updated at least once a year.” That is the floor. The ICO’s guidance is the more useful operating rule because it says privacy information should be updated before you start using personal data for a new purpose and that you should proactively bring that change to people’s attention first.
So a stronger privacy policy generator for bloggers workflow triggers review when:
- a new newsletter or CRM tool goes live;
- a new ad, analytics, or affiliate platform starts receiving data;
- a new embedded-media or community tool is added;
- the cookie banner or preference flow changes;
- the rights-request route changes; or
- the blog expands into a new audience, region, or product flow.
If policy review is not tied to release work, it usually falls behind production reality.
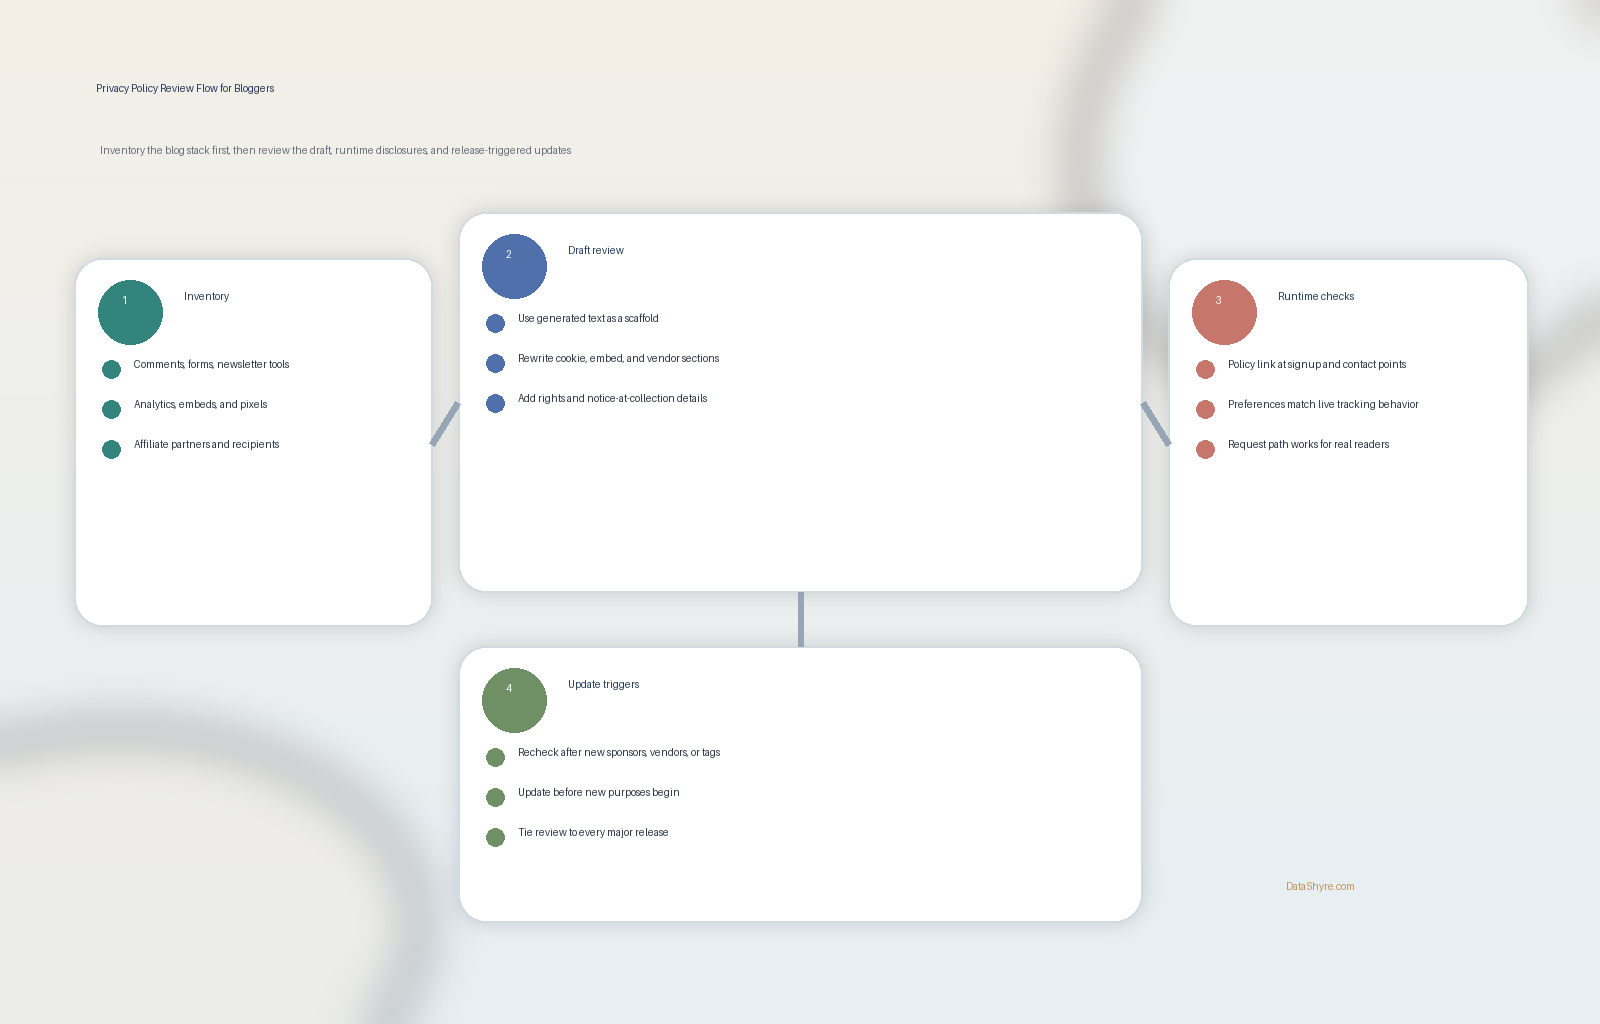
A practical 7-step review for this week
If you were reviewing a privacy policy generator for bloggers draft today, use this order:
- map the live blog stack first;
- generate or collect the draft text;
- rewrite the draft so it matches the real collection points and vendors;
- test whether notices and links appear where readers actually submit data;
- verify cookies, embeds, affiliate tooling, and preference controls;
- test the rights path the page describes; and
- tie future stack changes to a required policy review.
That order catches more real problems than polishing template language first.
FAQ
Is a privacy policy generator for bloggers enough by itself?
No. It can speed up drafting, but it cannot confirm your live forms, newsletter stack, cookies, embeds, vendors, or rights workflow on its own.
Do bloggers need to mention embedded tools and affiliate-related tooling?
If those tools collect data, drop identifiers, or send information to third parties, the privacy policy should describe them honestly instead of hiding them under generic labels.
Does a blog privacy policy only need an annual review?
No. Annual review is a minimum cadence. The safer operating model is to review the page whenever the blog starts a new data use, adds a new tool, or changes the rights or consent path.
Bottom line
The best privacy policy generator for bloggers in 2026 is not the one that produces the cleanest first draft.
It is the one you treat as a starting point while you verify the live forms, newsletter tools, cookies, embeds, affiliate tooling, and reader-rights path behind the blog.
If those checks are weak, the generated page is not a privacy program.
The fastest way to judge privacy policy generator for bloggers is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- California Department of Justice, California Consumer Privacy Act (CCPA): https://oag.ca.gov/privacy/ccpa
- California Department of Justice, How to Read a Privacy Policy: https://www.oag.ca.gov/privacy/facts/online-privacy/privacy-policy
- California Privacy Protection Agency, FAQs: https://cppa.ca.gov/faq.html
- EUR-Lex, Regulation (EU) 2016/679, Article 12: https://eur-lex.europa.eu/eli/reg/2016/679/oj/eng/
- FTC Consumer Advice for Business, Privacy and Security: https://consumer.ftc.gov/business-guidance/privacy-security
- ICO, How should we draft our privacy information?: https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/individual-rights/the-right-to-be-informed/how-should-we-draft-our-privacy-information/
- WordPress Documentation, Settings Privacy screen: https://wordpress.org/documentation/article/settings-privacy-screen/
- WordPress Documentation, WordPress Privacy: https://wordpress.org/documentation/article/wordpress-privacy/