GDPR Policy Generator in 2026: What It Covers, What It Misses, and 7 Live Checks
The real value in gdpr policy generator shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for gdpr policy generator is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
That is the real risk in 2026.
A gdpr policy generator can help structure a notice, but it cannot see your live website journey, your real vendor stack, your cookies and embeds, or the way your rights path actually works after someone clicks the footer.
The current official sources still point in that direction. Article 12 GDPR says the information must be provided in a “concise, transparent, intelligible and easily accessible form, using clear and plain language.” The European Commission still says people should be told, among other things, the purposes, categories of data, legal basis, retention period, recipients, international transfers where relevant, and their basic rights. The ICO also says that if you plan to use personal data for a new purpose, you must update the privacy information and “proactively bring this change to their attention before you start any new processing.”
So the test for a useful gdpr policy generator is not whether it creates a polished page.
It is whether the page still matches the real processing by the time it goes live.
If you want nearby context first, start with these guides to privacy policy template for website, gdpr requirements, and cookie policy. This page stays narrower. It is the gdpr policy generator review I would use this week before publishing generator output on a live site.
If your team is trying to get gdpr policy generator under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
1. Start with the live processing map, not the generated text
The most common gdpr policy generator failure is trusting the draft before anyone checks the product.
That reverses the right order.
The generator can only work from what it is told.
It cannot discover the real contact forms, product telemetry, support tools, CRMs, cookies, embedded video, chat widgets, or mobile download paths unless someone maps them first.
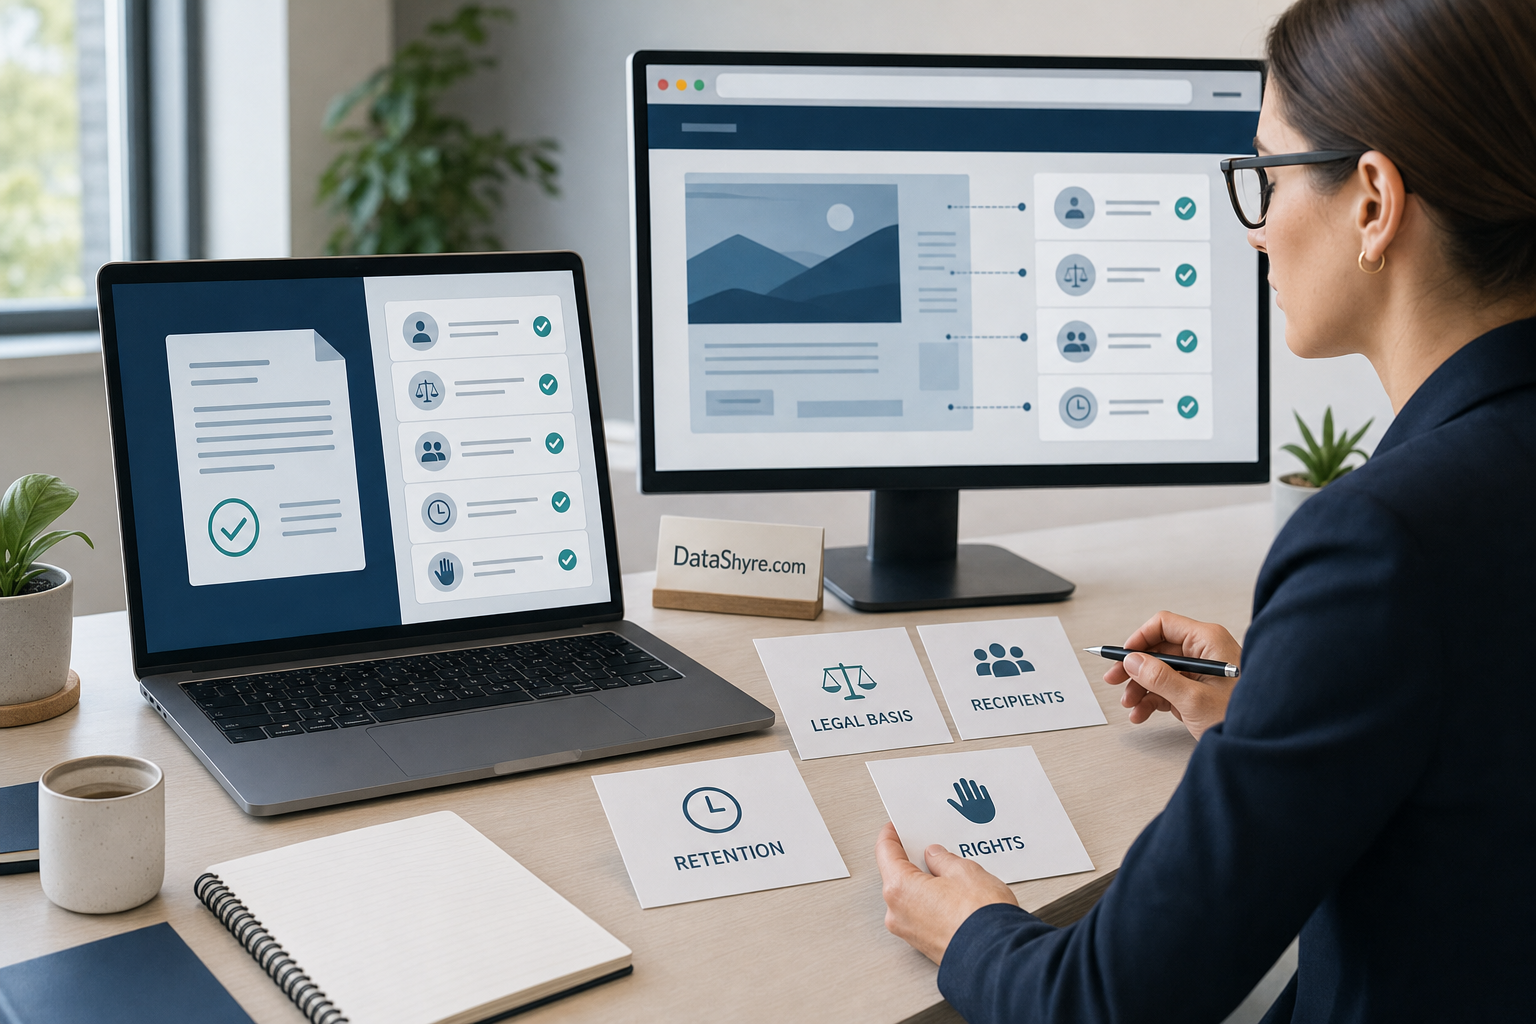
That matters because the European Commission still lists the actual notice blocks people have to receive, including purposes, legal basis, categories of data, retention, recipients, transfer information where relevant, and rights.
So before reviewing any gdpr policy generator output, confirm:
- what collection points exist on the live site or app;
- what personal data each point collects;
- why each category is collected;
- which systems or vendors receive it; and
- whether the draft reflects what really happens today.
If the live map is weak, the generated notice will only hide the weakness better.
2. Check whether the draft actually covers the Article 12 and 13 notice blocks
A polished gdpr policy generator page can still miss essential sections.
This is why structure matters more than style.
The European Commission’s current GDPR materials still summarize the notice duties in practical terms: identity of the organization, purposes, categories of data, legal basis, storage period, recipients, transfer information where relevant, and rights.
For a serious gdpr policy generator review, check whether the draft clearly covers:
- the controller identity and contact route;
- the specific purposes for each processing activity;
- the legal basis attached to those purposes;
- the categories of personal data involved;
- recipient categories or named processors where appropriate;
- transfer information outside the EU or UK where relevant;
- the retention period or the criteria used to decide it; and
- the rights available to the individual.
If the page sounds complete but cannot answer those questions cleanly, the generator did not finish the job.
3. Make sure the legal basis is tied to the real purpose, not pasted everywhere
This is where many gdpr policy generator drafts become vague very quickly.
The language looks formal, but the logic is thin.
The notice should not say only that data is processed to improve services or comply with the law.
It should reflect the real purpose behind the form, feature, cookie, or workflow.
A usable gdpr policy generator draft therefore needs review for:
- purpose statements that are specific enough to test;
- legal bases that match the actual activity;
- separate handling for analytics, marketing, support, security, and account functions;
- consent language that matches the actual consent flow where consent is relied on; and
- removal of broad filler that could hide incompatible reuse later.
If the purpose language is sloppy, the notice may stop being truthful the moment the business adds a new campaign or tool.
4. Do not let recipients, transfers, and retention stay generic
A weak gdpr policy generator often hides the most important operational facts behind phrases like trusted partners or we keep data as long as necessary.
That is not enough for a page that is supposed to inform someone properly.
The European Commission still lists recipients, transfer information where relevant, and storage duration among the core notice items. That means a generated draft should be tested against the actual vendor and infrastructure stack, not just approved for tone.
For a gdpr policy generator review, verify:
- which processors or recipient categories receive the data;
- whether any data is transferred outside the EU or UK;
- what safeguard language is needed where transfers exist;
- whether retention is stated clearly enough to be operational; and
- whether the retention statement matches the real product or support workflow.
This is where DataShyre can help if the live stack is messy. If your notice output looks clean but your recipients, scripts, or regional data routes are hard to trace, DataShyre can help map the flows and tighten the implementation before the page becomes a promise you cannot defend.
5. Turn the rights section into a route a person can actually use
Many gdpr policy generator drafts list rights correctly and still fail people in practice.
That happens when the rights section reads like a legal glossary instead of a working route.
The European Commission still explains that individuals should be told about their basic rights, including access, deletion, portability where relevant, and other controls available under the GDPR. In real deployments, that means the notice should point to a real submission path, not just name the rights abstractly.
So test whether the gdpr policy generator output explains:
- how someone can submit a request;
- where they can contact the organization or DPO if relevant;
- how consent can be withdrawn where consent is relied on;
- how cookie or privacy settings can be revisited later;
- whether identity verification or account routing changes the process; and
- whether the live page, inbox, or settings flow actually works.
If the rights paragraph sounds strong but the request path is confusing, the notice is incomplete in the place users care about most.
6. Review the runtime evidence for cookies, embeds, plugins, and third-party tools
This is the gap a gdpr policy generator can almost never close on its own.
The draft may look correct and still miss what the browser actually reveals.
If the site uses analytics tags, advertising tools, embedded video, social widgets, consent tools, chat, or WordPress plugins, those technologies can change the privacy facts without changing the draft prompt.
This is why I would always pair gdpr policy generator output with a live browser review:
- inspect cookies and similar technologies;
- check scripts and embeds that create extra data flows;
- compare vendor names and categories against the notice;
- confirm that consent-dependent tools do what the notice says they do; and
- revisit the notice after any plugin, tag-manager, or site release.
If you skip that step, the generated page may describe last month’s website instead of today’s.
7. Add update triggers before the next product change makes the draft false
The biggest long-term weakness of a gdpr policy generator is drift.
A draft can be right on launch day and false a week later.
The ICO’s current guidance is explicit here. If you plan to use personal data for a new purpose, you must update the privacy information and bring the change to people before the new processing starts.
That means a gdpr policy generator workflow should not end with publish.
It should trigger review when:
- a new vendor, plugin, SDK, or embed is added;
- a form starts collecting new fields;
- the business starts a new marketing or analytics use case;
- international transfer details change;
- the rights route or DPO contact path changes; or
- the consent or preference center experience changes.
That review loop matters more than whether the first draft came from a generator or a human.
A practical review order for this week
If I were checking gdpr policy generator output today, I would use this order:
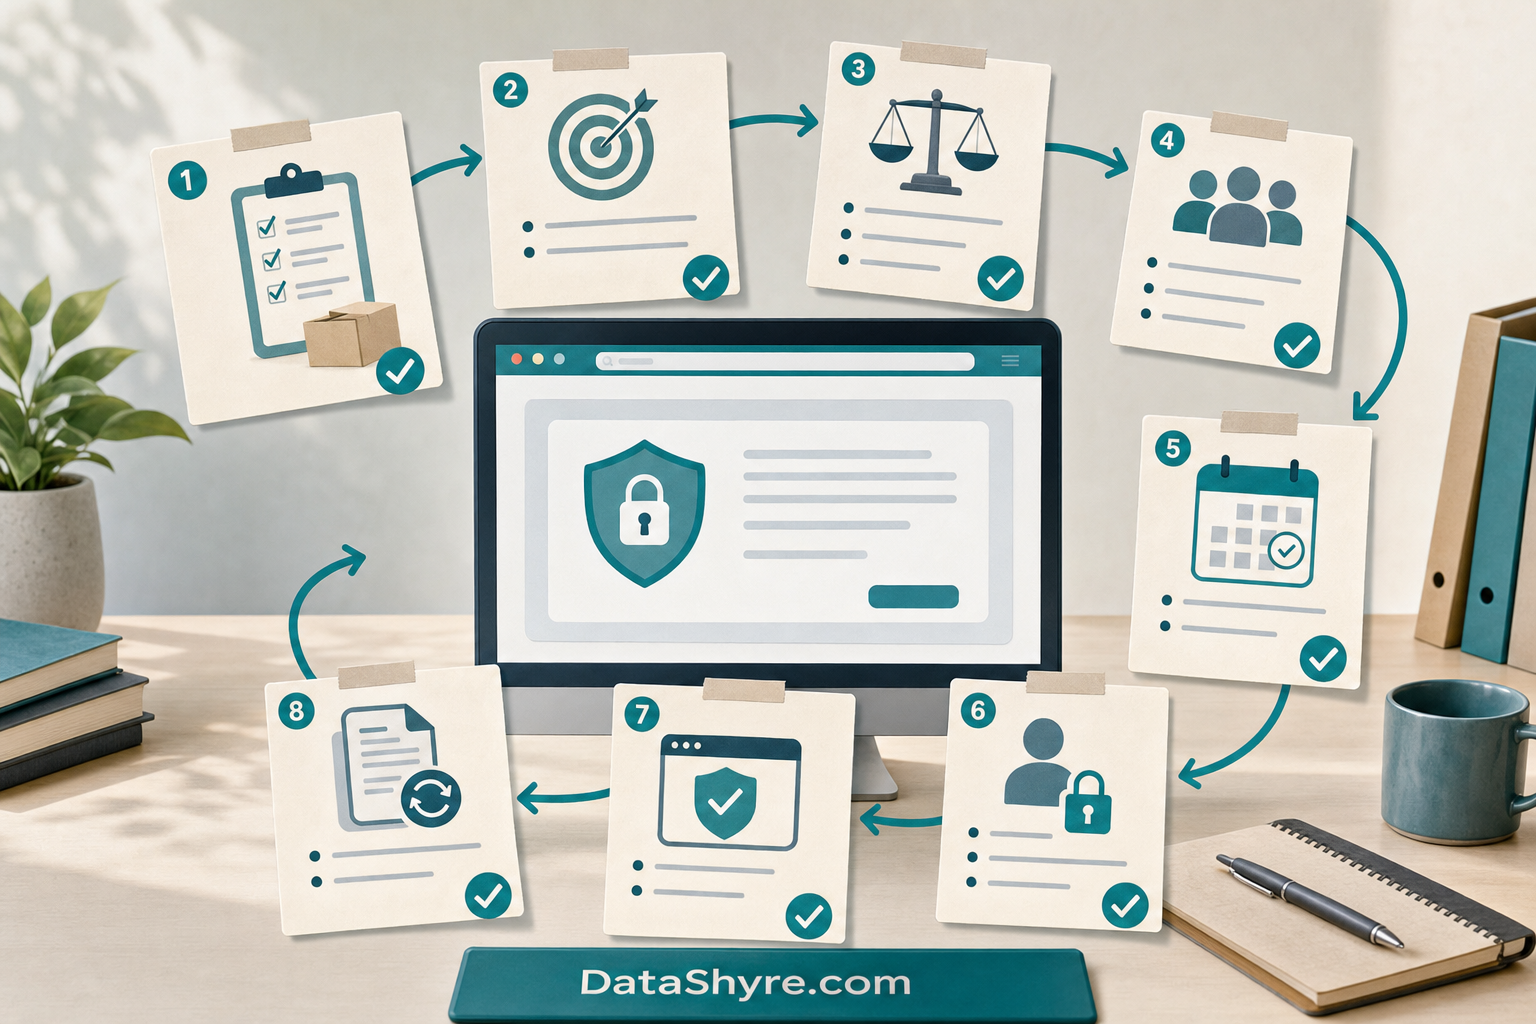
- map the live collection and processing points first;
- confirm the Article 12 and 13 notice blocks are all present;
- tie each purpose to the right legal basis;
- verify recipients, transfers, and retention against the real stack;
- test the rights and withdrawal path as a user;
- compare the page against runtime evidence from cookies, embeds, and plugins; and
- assign update triggers before the next release.
That sequence usually catches the dangerous gaps faster than copy-editing the notice first.
FAQ
Is a GDPR policy generator enough on its own?
No. A gdpr policy generator can speed up drafting, but it cannot verify the real processing map, browser-side behavior, vendor stack, or rights path by itself.
Can a GDPR policy generator write a compliant notice automatically?
Not safely without review. It can help structure the notice, but the final page still has to match the actual purposes, legal basis, recipients, transfers, retention logic, and user controls in production.
When should I update a generated GDPR privacy notice?
Update it whenever the underlying processing changes, especially after new vendors, forms, analytics uses, transfer changes, or rights-path changes are introduced.
Bottom line
The best gdpr policy generator in 2026 is not the one that writes the fastest.
The fastest way to judge gdpr policy generator is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- GDPR text, Article 12 and related notice duties: https://eur-lex.europa.eu/eli/reg/2016/679/
- European Commission, obligations for organizations under the GDPR: https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/obligations_en
- European Commission, information for individuals and the right to be informed: https://commission.europa.eu/law/law-topic/data-protection/information-individuals_en
- ICO, how to draft privacy information and how to handle new purposes: https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/individual-rights/the-right-to-be-informed/how-should-we-draft-our-privacy-information/