Cookies Website in 2026: What Website Cookies Actually Do and 7 Live Checks
The real value in cookies website shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for cookies website is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
It is also too small for the real review.
In 2026, a practical cookies website review has to ask at least four questions at once:
- what the cookie actually does;
- whether it is necessary or optional;
- whether another company receives data through it; and
- whether consent, opt-out, or browser controls really change the live behavior.
If you want nearby explainers first, start with these guides to browser cookies, third party cookies, and website privacy checker. This page stays narrower. It is the cookies website review I would use this week before telling a team that the site is under control.
If your team is trying to get cookies website under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
The timing matters. The FTC’s current consumer guidance still says websites and apps may track people with a cookie or pixel even after they leave the site. The ICO finalized its storage-and-access-technologies guidance on April 29, 2026, making clear that the operational review now extends beyond classic cookies to tracking pixels, device fingerprinting, scripts, tags, and similar techniques. California’s Department of Justice still describes Global Privacy Control as a “stop selling or sharing my data switch.” And on October 29, 2026, France’s CNIL published details of a 7 million euro sanction imposed on October 22, 2026 against FNAC DARTY entities over cookie and tracking-device failures in a mobile-app context.
1. Start with what website cookies actually do
At the browser level, website cookies are still a simple mechanism.
MDN’s current HTTP references explain that a server can send a Set-Cookie header in a response and the browser can later return that value in the Cookie request header.
That mechanism lets website cookies support things like:
- keeping a user signed in;
- remembering language or display preferences;
- preserving a shopping cart;
- storing a consent or notice choice; and
- supporting analytics or advertising workflows.
The mechanism itself is not the problem.
The review starts with purpose.
2. Separate necessary cookies from optional tracking
Most cookies website questions are not really definition questions.
They are purpose questions.
A practical review usually separates website cookies into groups like:
- necessary or security cookies for login, fraud prevention, checkout continuity, or load balancing;
- preference cookies for language, region, or remembered settings;
- analytics cookies for measuring visits or behavior; and
- advertising or profiling cookies for attribution, audience building, or cross-context recognition.
The FTC’s consumer guidance still uses that broader everyday framing. It explains that websites and apps use cookies, pixels, and device fingerprinting to remember preferences, gather analytics, and personalize advertising.
This is why the right cookies website question is not only Is there a cookie?
It is Why is it there, and what changes if the user says no?
3. Do not let first-party versus third-party be the only test
Teams often explain website cookies by splitting them into first-party and third-party categories.
That distinction still helps, but it does not finish the job.
Chrome’s current developer documentation still treats third-party cookies as those set by a site different from the top-level page, and it exposes them clearly in DevTools. That is useful.
But an operational cookies website review should go one step further and ask:
- who sets the cookie;
- who receives the resulting data;
- whether the cookie supports security, convenience, measurement, or profiling;
- whether the site still works without it; and
- whether some other storage or access technology is doing the same thing anyway.
If you stop at the label alone, you can miss the real tracking path.
4. Remember cookies are only one part of the tracking stack
This is where older articles about cookies website usually go stale.
The ICO’s finalized 2026 guidance is explicit that PECR applies more broadly to storage and access technologies, not just classic cookies. Its guidance covers cookies, tracking pixels, link decoration and navigational tracking, device fingerprinting, web storage, and scripts or tags.
That matters because a site can look cleaner in a cookie table while still passing user data through other mechanisms.
So when someone says their cookies website setup is under control, I would not stop at the cookie names in the browser.
I would also inspect:
- network requests before any choice is made;
- tag-manager behavior;
- embedded chat, video, and social widgets;
- local storage and similar client-side persistence; and
- whether vendors begin receiving identifiers before the user makes a real choice.
5. Treat consent and opt-out as regional branches, not one global answer
This is one of the biggest practical mistakes teams make with cookies website reviews.
There is no single worldwide rule.
EU and UK branch
The ICO’s current guidance says a person must receive clear information and, unless an exemption applies, consent must be obtained before storage and access technologies are used. For many EU- or UK-facing setups, that means optional analytics, advertising, and profiling technologies should not start by default.
The latest enforcement pattern still lines up with that principle. In the FNAC DARTY case announced on October 29, 2026, the CNIL said the companies used a tracker in their mobile app without consent, collected browsing history, and used the resulting data to personalize product recommendations and train the recommendation algorithm.
California branch
California often changes the practical question.
The California DOJ says businesses that sell or share personal information must offer methods for consumers to opt out, and that a user-enabled Global Privacy Control can function as a “stop selling or sharing my data switch.” The CPPA’s current FAQs also say businesses must honor qualifying opt-out preference signals such as GPC and, in most instances, provide a clear and conspicuous website link labeled Do Not Sell or Share My Personal Information, Your Privacy Choices, or Your California Privacy Choices.
So for California-facing cookies website reviews, the core test is often not Do we have an EU-style banner?
It is:
- whether the notice at collection is accurate;
- whether an opt-out of sale or sharing exists where required;
- whether GPC is honored where applicable; and
- whether downstream advertising or sharing behavior actually changes.
Copied banner design is not enough if the runtime path does not change.
6. Check security settings and lifetimes, not only notice copy
Not every website-cookies issue is a consent issue.
Some are basic security issues.
MDN’s current secure-cookie guidance still recommends deliberate use of Secure, HttpOnly, tighter Domain and Path scope, and SameSite settings. It also recommends Host- and Secure- prefixes where they fit.
That means if website cookies support sessions, accounts, or sensitive workflows, I would check at least:
- whether
Secureis present; - whether
HttpOnlyis present where it should be; - whether
SameSiteis deliberate rather than accidental; - whether the scope is broader than necessary; and
- whether the lifetime fits the actual risk.
Weak session-cookie hygiene and weak privacy hygiene often show up together.
7. Test the live browser behavior instead of trusting the spreadsheet
The strongest cookies website review is not a policy review and not a cookie export alone.
It is a runtime test.
Chrome’s current DevTools documentation still gives teams a direct way to inspect cookie fields such as expiry, HttpOnly, Secure, SameSite, and partition state. That is useful because real website-cookies behavior often looks different once you test:
- the no-choice path;
- the reject path;
- the accept path;
- the later-withdrawal path;
- California opt-out and GPC behavior where relevant;
- more than one browser; and
- what happens again after the next deployment.
That is how hidden leaks and timing problems show up.
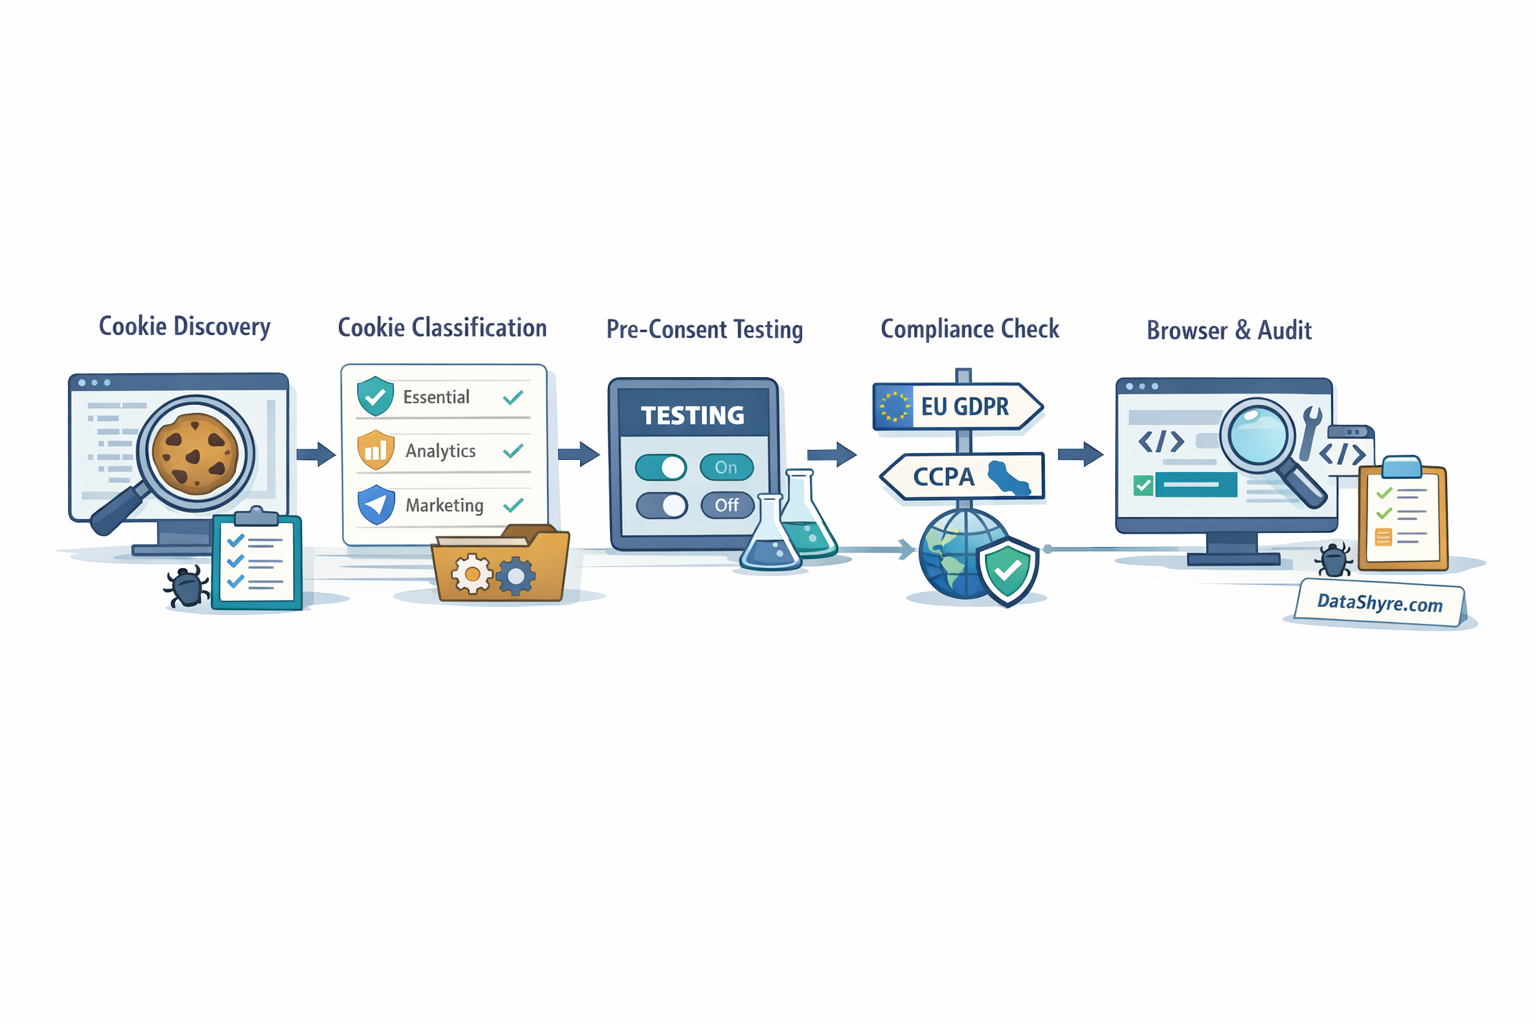
A practical 7-step cookies website review
If I were auditing a cookies website setup this week, I would use this order:
- list every cookie and adjacent storage or access technology that appears before user choice;
- classify each item as necessary, preference, analytics, advertising, or embedded-third-party behavior;
- identify which vendors receive data and which tools write identifiers;
- test reject, accept, category-level choices, and later withdrawal;
- test California opt-out and GPC behavior if sale or sharing is in scope;
- review security settings on session and account cookies; and
- compare the live findings against the notice, privacy policy, and consent interface.
That sequence usually reveals more truth than a policy rewrite alone.
FAQ
Are cookies website and website cookies the same thing?
Usually, yes in everyday usage. Cookies website is an awkward search phrase, while website cookies is the more natural wording. In real deployments, people usually mean the same browser-storage mechanism and the same compliance questions around it.
Do all website cookies need consent?
No. Some cookies can be exempt because they are strictly necessary for the service the user requested. The higher-risk branch is usually optional analytics, advertising, profiling, or similar tracking behavior.
If I delete website cookies, does that stop all tracking?
Not necessarily. The ICO’s current guidance is explicit that the review is broader than cookies alone. A site can reduce visible cookies while still using pixels, scripts, web storage, or fingerprinting to pursue similar tracking outcomes.
Bottom line
The safest way to think about a cookies website review in 2026 is not tiny files that only matter to banner lawyers.
It is one browser-level memory mechanism inside a broader runtime, security, and compliance system.
If you know what each cookie does, who receives the data, what changes after consent or opt-out, how other storage technologies interact with it, and whether the browser configuration is sound, you are much closer to the truth.
The fastest way to judge cookies website is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- FTC Consumer Advice, How Websites and Apps Collect and Use Your Information: https://consumer.ftc.gov/articles/how-websites-and-apps-collect-and-use-your-information
- MDN, Set-Cookie header: https://developer.mozilla.org/en-US/docs/Web/HTTP/Reference/Headers/Set-Cookie
- MDN, Cookie header: https://developer.mozilla.org/en-US/docs/Web/HTTP/Reference/Headers/Cookie
- MDN, Secure cookie configuration: https://developer.mozilla.org/en-US/docs/Web/Security/Practical_implementation_guides/Cookies
- Chrome for Developers, View, add, edit, and delete cookies: https://developer.chrome.com/docs/devtools/application/cookies/
- ICO, Final storage and access technologies guidance published, April 29, 2026: https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- ICO, What are storage and access technologies?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/what-are-storage-and-access-technologies/
- ICO, How do we comply with the PECR rules?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/how-do-we-comply-with-the-pecr-rules/
- California Department of Justice, California Consumer Privacy Act (updated August 28, 2026): https://oag.ca.gov/privacy/ccpa
- California Department of Justice, Global Privacy Control (GPC): https://oag.ca.gov/privacy/ccpa/gpc
- California Privacy Protection Agency, FAQs: https://cppa.ca.gov/faq
- CNIL, Cookies and mobile application: 7 million euros fine against FNAC DARTY PARTICIPATIONS ET SERVICES and FNAC DIRECT, published October 29, 2026: https://www.cnil.fr/en/sanction-app-cookies-fnac