Cookie Consent Management Tool in 2026: 8 Live Checks Before You Trust One
The real value in cookie consent management tool shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for cookie consent management tool is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
A cookie consent management tool only earns trust if it changes live behavior before optional technologies start, gives people a real refusal path, handles regional branches on purpose, and leaves behind proof another team can still understand later.
That is still the direction of the current official materials. The European Commission says valid consent should use “clear and plain language” and that withdrawal should be possible through a method “as easy to use as giving consent.” The EDPB’s current consent summary still says passive behavior like scrolling is not a “clear affirmative action.” CNIL still states the clearest first-layer rule in one sentence: rejecting cookies should be “just as easy as accepting them.” Google’s current setup guide still says denied defaults must be set “before any commands that send measurement data.” And California’s DOJ still describes Global Privacy Control as a “stop selling or sharing my data switch.”
If you want nearby context first, start with these guides to cookie consent management, cookie consent requirements, and consent management platform. This page is narrower. It is the live review I would use this week before trusting a cookie consent management tool on a real site.
If your team is trying to get cookie consent management tool under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
1. Judge the control path, not the feature list
The first cookie consent management tool mistake is treating the product page as the implementation.
What matters on a live site is the control path:
- how the default state is set before any choice;
- which tags, scripts, pixels, and embeds read that state;
- where region logic branches;
- how later withdrawal is handled; and
- what evidence the tool stores when the choice changes.
If a cookie consent management tool cannot explain that path cleanly, the polished interface matters less than teams think.
2. Test the no-choice state before you test acceptance
This is still the fastest way to find whether the tool is actually controlling anything.
The ICO’s finalized 2026 storage-and-access-technologies guidance now expressly covers cookies, scripts, tags, tracking pixels, and fingerprinting, not only the cookie table many teams still focus on. Google’s current documentation points to the same operational reality from another angle: denied defaults should land “before any commands that send measurement data.”
So for any cookie consent management tool, start in a fresh browser session and test:
- first load with no interaction;
- navigation to a second page without choosing;
- mobile behavior, not only desktop behavior; and
- pages with heavier embeds, chat, video, or marketing tags.
If optional technologies are already active before the user decides, the tool is not doing the job the interface implies.
3. Make refusal as real as acceptance
This is where many weak tools still rely on friction.
CNIL’s notice on dark patterns says “rejecting cookies should be just as easy as accepting them.” That should affect how you evaluate a cookie consent management tool, not only how you write banner copy.
Check whether the tool makes it practical to:
- show
Reject allwhereAccept allappears; - keep the same balance on mobile layouts;
- avoid visual weighting that quietly pushes acceptance; and
- reopen settings later without hiding the route.
A cookie consent management tool that can only produce a strong accept path is not strong where it matters.
4. Split categories and purposes clearly
The European Commission still ties valid consent to specificity, and the EDPB’s materials keep the same principle in plain language: multiple purposes should not be blurred into one vague yes.
So a serious cookie consent management tool should let teams separate at least some of these branches where relevant:
- necessary functions;
- analytics;
- advertising or retargeting;
- personalization;
- embedded third-party media; and
- any separate sale-or-sharing or partner-sharing logic.
The useful test is not how elegant the settings drawer looks. It is whether a normal person could explain what changes if they enable one category and refuse another.
5. Run regional branches on purpose
One cookie consent management tool should not flatten every jurisdiction into one assumed flow.
For EU and UK traffic, the main issue is often prior consent for non-essential storage or access technologies. In California, the live issue is often whether opt-out of sale or sharing actually works, including when a browser sends GPC. The California DOJ still frames GPC as a “stop selling or sharing my data switch,” which is a different operational branch from EU or UK affirmative opt-in for non-essential tracking.
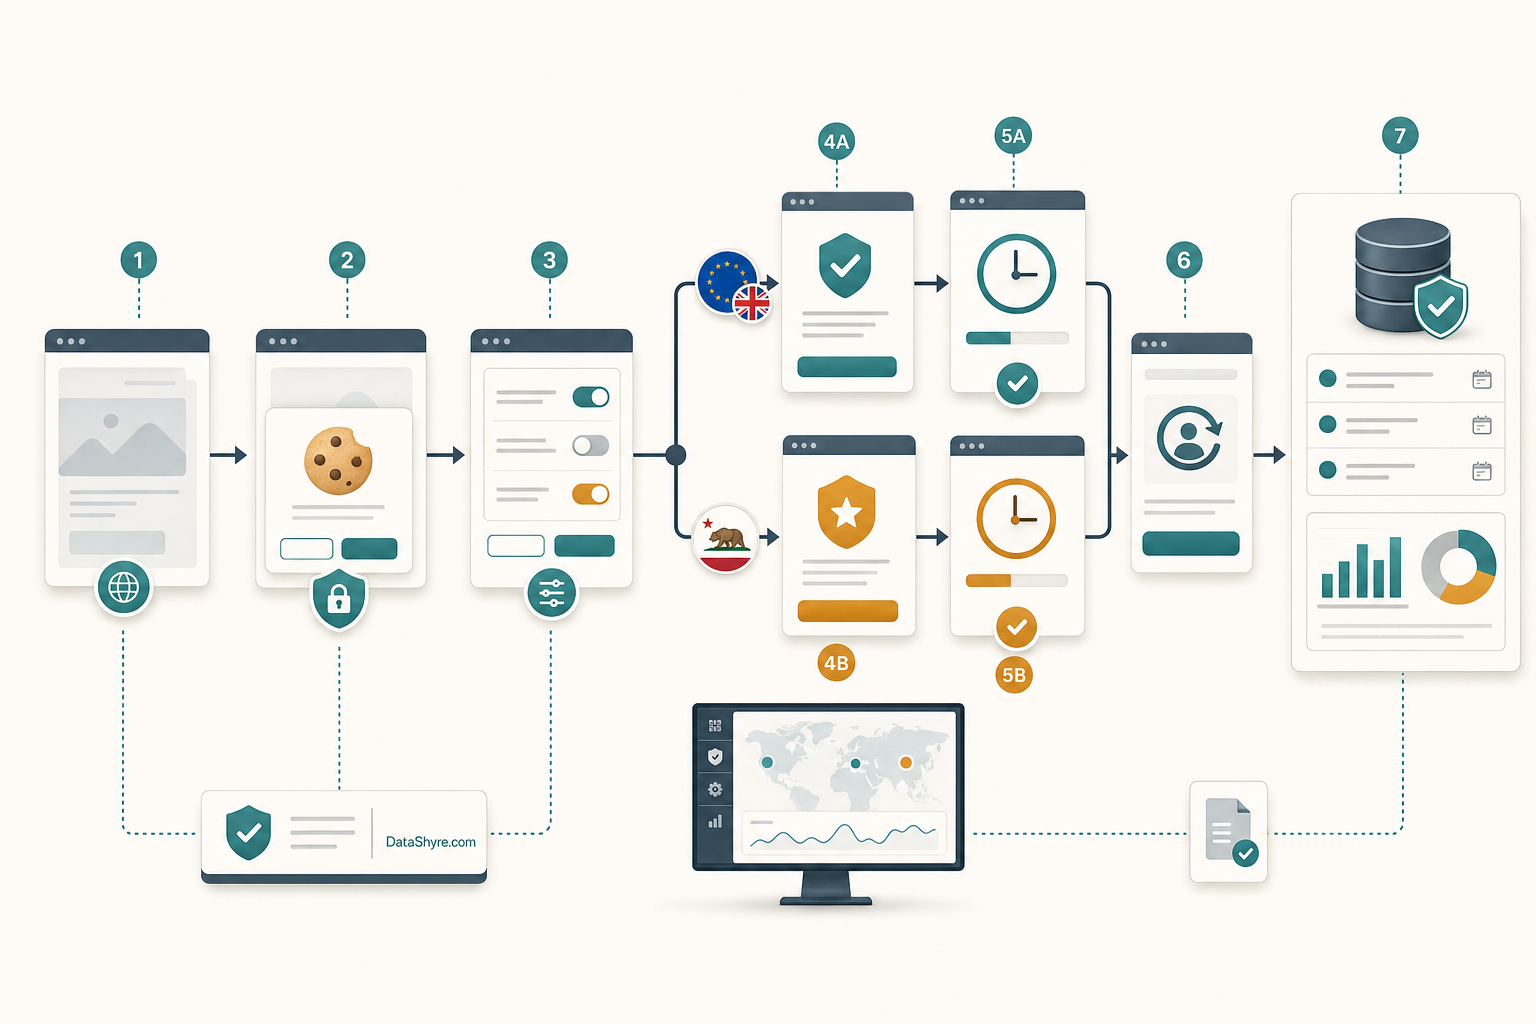
That means a real cookie consent management tool review should test separate branches for:
- EU or UK prior consent;
- California opt-out of sale or sharing;
- GPC handling;
- reopened settings and withdrawal; and
- any logged-in or cross-property propagation path.
One banner can front those branches. One branch should not be mistaken for all of them.
6. If Google tags or publisher ads matter, test that branch separately
This is where a cookie consent management tool can look complete in the dashboard and still fail in the browser.
Google’s current guidance still says the default consent command should run on every page “before any commands that send measurement data.” Separately, Google’s AdSense guidance still says publishers serving personalized ads in the EEA, UK, or Switzerland must use a Google-certified CMP integrated with the IAB TCF.
That creates at least two distinct checks:
- whether Google tags honor denied defaults before any data-sending command runs; and
- whether the publisher branch needs Google’s certified-CMP requirements where monetization rules apply.
A cookie consent management tool should be able to support both reviews without pretending they are the same question.
7. Verify that choices travel as far as the data does
This is one of the most important operational tests.
On February 11, 2026, California Attorney General Rob Bonta announced a $2.75 million settlement with Disney over allegations that opt-out requests were not fully effectuated across devices and streaming services associated with consumers’ accounts. That was not a banner cosmetics problem. It was a propagation problem.
The same lesson applies to any cookie consent management tool. Test whether a choice actually reaches:
- tag managers;
- analytics and advertising tools;
- embedded vendors;
- account-linked experiences;
- connected properties where relevant; and
- suppression logic tied to California opt-outs or similar privacy states.
If the first screen changes but the downstream behavior does not, the tool has not finished the job.
8. Buy for operations, not only launch-day setup
The strongest cookie consent management tool is rarely just the one with the prettiest banner builder.
It is the one that helps the team operate the control over time:
- version the notice and settings shown;
- log accept, reject, withdrawal, and GPC events in a usable way;
- expose enough detail to investigate incidents after a release;
- survive tag changes, new embeds, and vendor additions; and
- make retesting part of the routine instead of an annual cleanup project.
That matters because privacy failures often appear after an ordinary deployment, not on the day the tool is first switched on.
A practical review order for this week
If I were auditing a cookie consent management tool today, I would use this order:
- map the control path from first layer to downstream systems;
- test the no-choice state before acceptance;
- compare refusal and acceptance on desktop and mobile;
- inspect category specificity;
- run EU or UK, California, and Google-specific branches separately where relevant;
- verify propagation across vendors and connected properties; and
- save proof before the next release changes the behavior.
That sequence usually finds the real weakness faster than another round of banner editing.
FAQ
Is a cookie consent management tool basically the same as a banner?
No. A banner is only one interface layer. A cookie consent management tool also needs to control runtime behavior, regional logic, withdrawal, and evidence.
Can one tool handle both EU consent and California opt-out?
It can, but only if the implementation deliberately tests and configures those branches instead of assuming one path covers both.
Does Google Consent Mode replace a cookie consent management tool?
No. It helps with the Google measurement and advertising path, but it does not automatically solve non-Google tags, UI fairness, category design, or broader legal review by itself.
Bottom line
The best cookie consent management tool in 2026 is not the one with the longest checklist.
It is the one that keeps optional technologies off until the right signal exists, gives people a real refusal path, handles regional branches deliberately, supports Google timing where relevant, propagates the choice as far as the data goes, and leaves behind proof another team can still trust later.
The fastest way to judge cookie consent management tool is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- European Commission, legal grounds for processing data: https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/legal-grounds-processing-data_en
- European Data Protection Board, Summary: Consent under GDPR, when to act and what to do (PDF): https://www.edpb.europa.eu/system/files/2026-04/edpb-summary-consent_en.pdf
- UK Information Commissioner’s Office, guidance on the use of storage and access technologies: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/
- UK Information Commissioner’s Office, final storage and access technologies guidance published: https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- CNIL, dark patterns in cookie banners: https://www.cnil.fr/en/dark-patterns-cookie-banners-cnil-issues-formal-notice-website-publishers
- Google for Developers, set up consent mode on websites: https://developers.google.com/tag-platform/security/guides/consent
- Google AdSense Help, Google consent management requirements for serving ads in the EEA, the UK, and Switzerland (for publishers): https://support.google.com/adsense/answer/13554116
- California Department of Justice, California Consumer Privacy Act (CCPA): https://oag.ca.gov/privacy/ccpa
- California Department of Justice, Global Privacy Control: https://oag.ca.gov/privacy/ccpa/gpc
- California Department of Justice, Attorney General Bonta announces $2.75 million settlement with Disney: https://oag.ca.gov/news/press-releases/california-wont-let-it-go-attorney-general-bonta-announces-275-million
- California Privacy Protection Agency, Enforcement Advisory No. 2024-02: avoiding dark patterns: https://cppa.ca.gov/pdf/enfadvisory202402.pdf
—
Published: October 28, 2026. Updated using current official regulator, government, and platform materials available at publication time.