CCPA California in 2026: 7 Live Checks for Scope, Notices, Opt-Outs, and Proof
The real value in ccpa california shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for ccpa california is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
The real test is whether the live business can explain what it collects, show the right notices, honor opt-out and correction requests, recognize browser signals, avoid manipulative choice design, and prove that the request actually changed downstream behavior.
That is the useful frame right now because California’s privacy rules are active on several fronts at once. The CPPA’s updated regulations took effect on January 1, 2026. Attorney General Rob Bonta announced a $2.75 million Disney settlement on February 11, 2026 over opt-outs that did not fully carry across services. The state then announced a $12.75 million GM settlement on May 8, 2026, describing it as the largest CCPA penalty in California history to date and its first data-minimization case. And on October 29, 2026, the Attorney General announced a $1.8 million Lyft settlement that focused on opt-out friction and unnecessary roadblocks in the app flow.
If you want nearby guides first, start with our posts on CCPA compliance, California web privacy law, and California data privacy protection act. This page stays broader. It is the ccpa california review I would use this week before telling leadership that the California program is in shape.
If your team is trying to get ccpa california under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
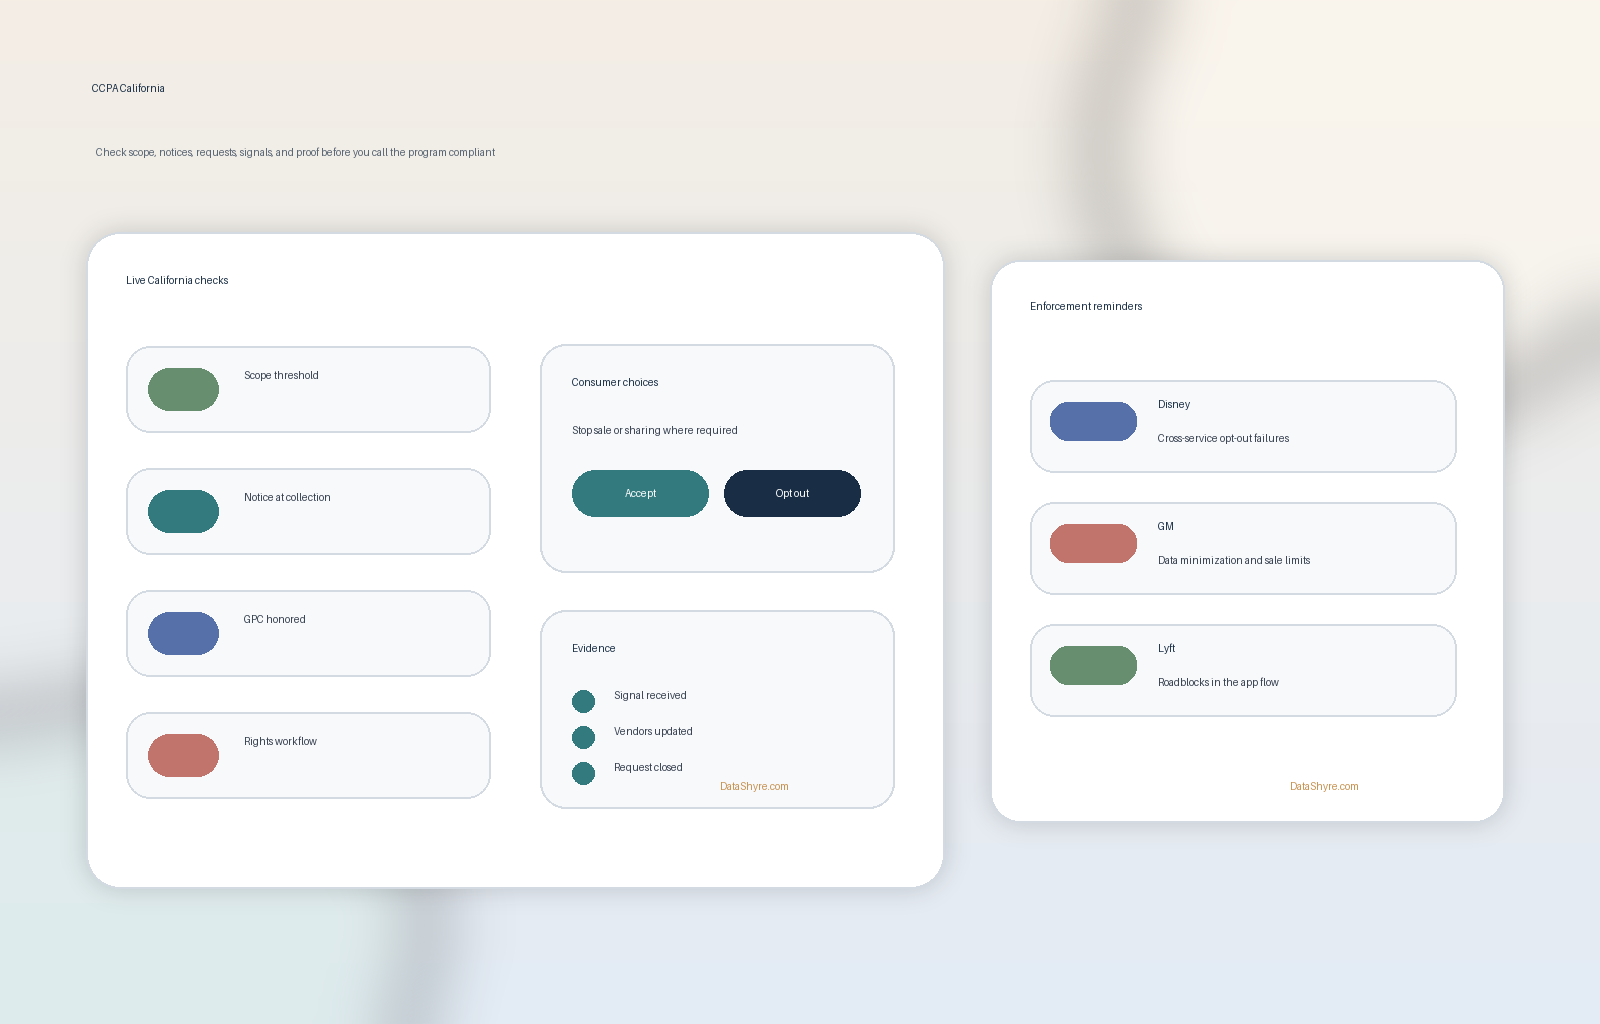
1. Confirm whether the business is actually in CCPA scope
Every serious ccpa california review starts with scope, because teams often keep repeating an answer that was never revisited after the business changed.
California’s Department of Justice still says the CCPA applies to for-profit businesses doing business in California that meet one of three common triggers:
- annual gross revenue above the threshold;
- buying, selling, or sharing the personal information of 100,000 or more California residents or households; or
- deriving 50 percent or more of annual revenue from selling California residents’ personal information.
The threshold question is worth tightening. The CPPA’s CPI adjustment page says the annual gross revenue threshold was updated to $26,625,000, effective January 1, 2025.
So the first ccpa california check is not only Do we think the law applies? It is:
- which legal entity is in scope;
- which threshold makes it in scope;
- which sites, apps, brands, or service surfaces are part of that answer; and
- whether that answer changed since the last audit.
If the scope map is fuzzy, everything that follows will be fuzzy too.
2. Match notice at collection and the privacy policy to the live stack
This is where many ccpa california programs start to drift.
The DOJ’s consumer guidance still says people must be told, before or at the point of collection, about the categories of personal information being collected and what may be done with that information. The same California guidance also says a business privacy policy has to explain consumer privacy rights and how to exercise them.
That means the review cannot stop at Do we have a privacy policy?
It has to ask whether the live system still matches:
- the categories collected;
- the purposes attached to each category;
- the categories of third parties receiving sold, shared, or disclosed data;
- whether sensitive personal information is used beyond limited purposes; and
- whether the listed request methods actually reach the right team.
The policy is not the control. The alignment is the control.
3. Make opt-out of sale or sharing and GPC work end to end
For many teams, this is where ccpa california fails in the browser instead of in the legal draft.
California’s DOJ still describes the Global Privacy Control as a:
“stop selling or sharing my data switch”
California Department of Justice
The CPPA FAQ also says businesses must honor qualifying opt-out preference signals, including GPC, as a valid request to opt out of sale or sharing.
That turns a vague privacy promise into a very concrete runtime test.
A useful ccpa california review should verify:
- whether the business sells or shares personal information at all;
- whether the opt-out path is clear and easy to use;
- whether GPC is detected and honored where required;
- whether the signal reaches downstream ad-tech, enrichment, and sharing flows; and
- whether the result persists across the account or service surface where the business actually sells or shares data.
The hard part is not the footer link. The hard part is whether the choice travels as far as the data does.
4. Remove dark patterns from the choice flow
A lot of ccpa california risk is now design risk.
The CPPA’s Enforcement Advisory No. 2024-02 tells businesses to use clear language and offer “symmetrical choices” when presenting privacy options. That matters because the state is not only reviewing whether a choice exists. It is reviewing whether the user interface subverts the user’s ability to make it.
In real deployments, a ccpa california review should check whether the live interface:
- hides the opt-out behind extra clicks or buried settings;
- makes acceptance visually easier than refusal;
- uses vague labels for privacy choices;
- breaks on mobile layouts or in-app webviews; or
- demands more information than the request actually needs.
That is also why the latest enforcement examples matter. On October 29, 2026, Attorney General Bonta said businesses cannot “throw up unnecessary roadblocks” when consumers try to exercise their California privacy rights, in connection with the Lyft settlement.
If the rights flow technically exists but is hard to find, hard to understand, or harder to use than the opposite choice, the program is weaker than it looks.
5. Run the full rights workflow, not just opt-out
The CCPA is broader than opt-out alone, and a useful ccpa california program has to act that way.
California’s current materials still point to the core rights to know, delete, correct, opt out of sale or sharing, limit the use and disclosure of sensitive personal information, and receive equal service and price without unlawful discrimination.
The CPPA FAQ also reminds businesses that requests to delete, correct, or know generally require at least two submission methods, including a toll-free number and, if the business has a website, a website method, unless the business operates exclusively online.
So a practical ccpa california review should test:
- how requests are submitted on web, app, and support surfaces;
- where identity verification is really needed and where it is not;
- how deletion, correction, and limit requests move through internal systems;
- how vendors are instructed when a request has to propagate; and
- what the completion record looks like after the work is done.
This is where many teams discover that the form exists, but the real process still depends on inboxes, spreadsheets, and guesswork.
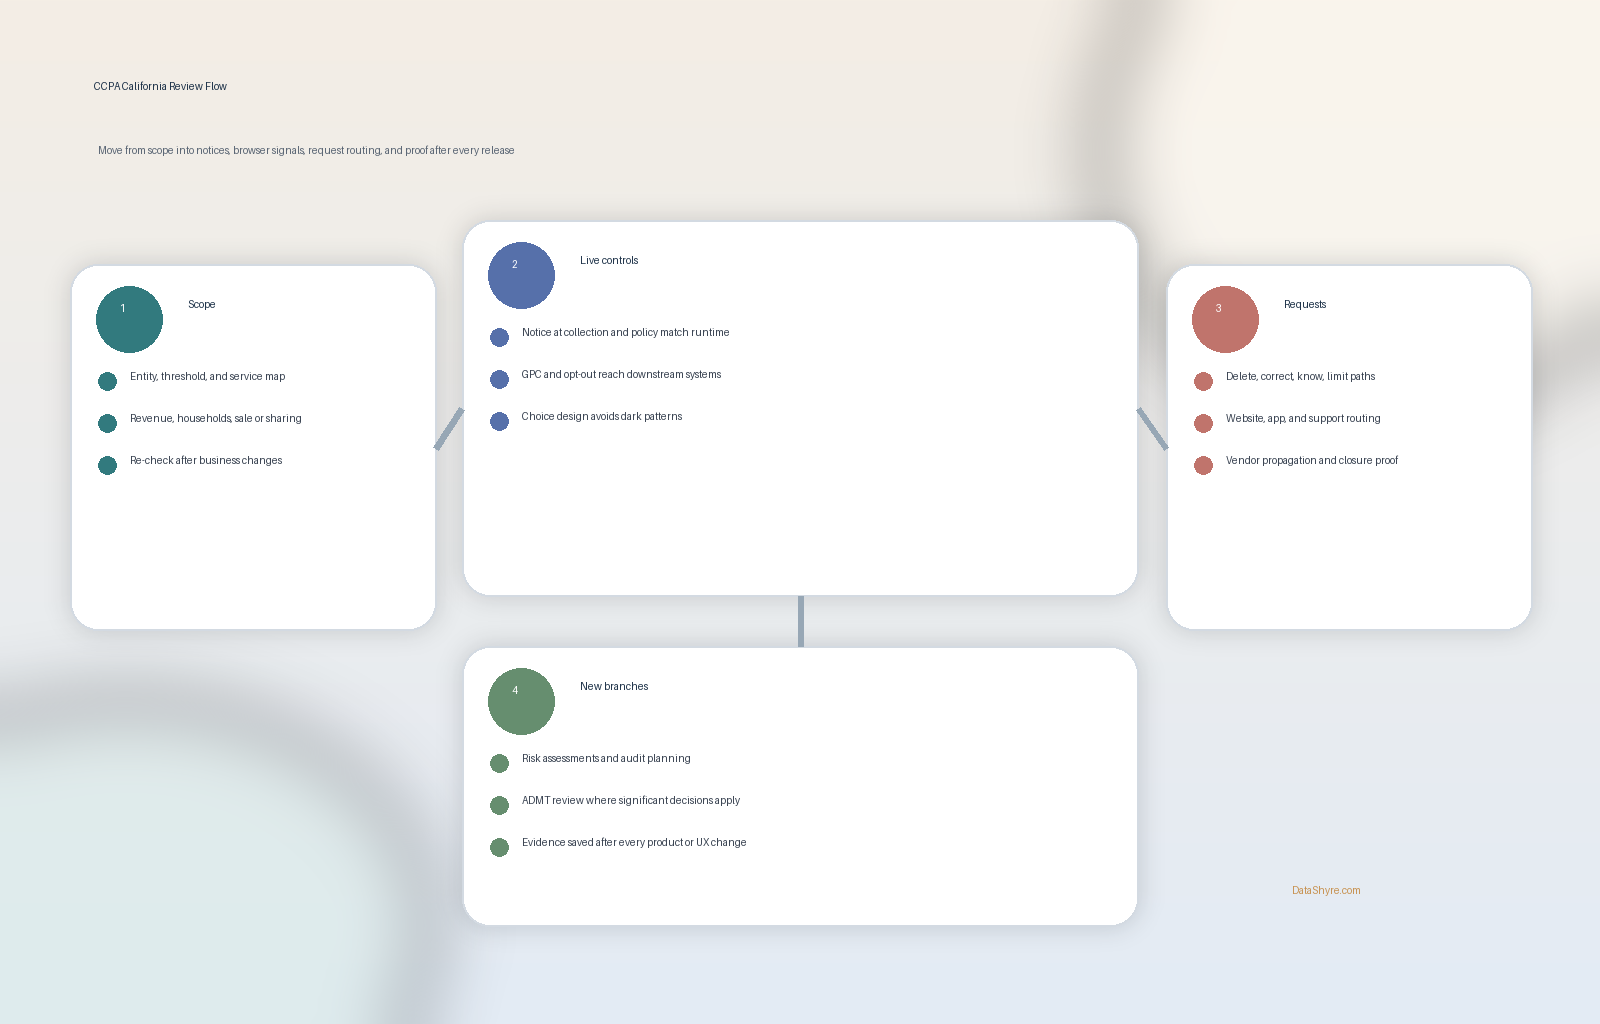
6. Follow the request across devices, apps, and linked services
This is one of the clearest operational lessons from recent ccpa california enforcement.
In the Disney settlement announcement on February 11, 2026, Attorney General Rob Bonta said a consumer’s opt-out right applies “wherever and however a business sells data.” The state said Disney failed to fully effectuate opt-out requests across services tied to a consumer’s account.
That means a strong ccpa california review cannot stop after one browser test.
It should verify whether a request or signal reaches:
- web properties and mobile apps;
- logged-in and logged-out experiences;
- connected services or linked brands where relevant;
- advertising, analytics, and partner flows downstream; and
- service providers or contractors supporting the business’s response.
If the user flips the switch on the first screen but the same sharing continues elsewhere, the request was not fully honored.
7. Add the newer CPPA branches and keep proof after every change
Older ccpa california checklists are often too short for late 2026.
The CPPA says its updated regulations covering CCPA updates, cybersecurity audits, risk assessments, ADMT, and insurance-company clarifications became effective on January 1, 2026. The agency also says businesses subject to risk-assessment requirements had to begin compliance on January 1, 2026, while certain ADMT requirements begin on January 1, 2027.
That means the better ccpa california question is no longer only Do we have notices and a request form?
It is also:
- do our processing activities trigger risk-assessment obligations;
- do we need cybersecurity-audit planning under the new rules;
- are any significant-decision uses of automated decisionmaking moving us into the 2027 branch; and
- do we keep evidence that shows the program still worked after product, vendor, or UX changes.
The GM settlement is the right reminder here. California described the case as the state’s first data-minimization action under the CCPA, which means the live question is not only what a business disclosed. It is also whether the business collected, kept, and shared more data than it should have.
A practical review order for this week
If I were auditing ccpa california today, I would use this order:
- confirm scope and the specific threshold basis;
- compare notice at collection and the privacy policy against live behavior;
- test opt-out of sale or sharing, including GPC;
- run correction, deletion, and limit-rights workflows end to end;
- review the choice architecture for dark-pattern risk;
- test whether requests propagate across services, vendors, and devices; and
- add the newer CPPA branches and save evidence before the next deployment changes the behavior.
That order usually surfaces the real problems faster than a policy rewrite alone.
FAQ
Does every California-facing website need full CCPA compliance?
No. A California-facing website will often still need a privacy policy and accurate disclosures, but full CCPA duties turn on whether the business is a covered for-profit business that meets the statutory thresholds.
Is CPRA a separate law from the CCPA?
Not in the way many teams talk about it. California’s official materials explain that the CPRA amended the CCPA and expanded it. In real deployments, most operating teams still talk about the current California framework as the CCPA.
Is a cookie banner enough for CCPA California compliance?
The fastest way to judge ccpa california is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- California DOJ: California Consumer Privacy Act (CCPA)
- California Privacy Protection Agency: FAQs
- California Privacy Protection Agency: Updated Monetary Thresholds in CCPA
- California Privacy Protection Agency: CCPA Updates, Cybersecurity Audits, Risk Assessments, Automated Decisionmaking Technology (ADMT), and Insurance Regulations
- California Privacy Protection Agency: CCPA statute and regulations effective January 1, 2026
- California Privacy Protection Agency Enforcement Division: Enforcement Advisory No. 2024-02
- California Attorney General: Disney settlement announcement, February 11, 2026
- California Attorney General: General Motors settlement announcement, May 8, 2026
- California Attorney General: Lyft settlement announcement, October 29, 2026
—
Published: October 30, 2026. Updated using current official California regulator, government, and enforcement materials available at publication time.