Privacy Statement for Website in 2026: What It Must Cover and 7 Live Checks Before You Publish
If you are searching for privacy statement for website guidance on November 15, 2026, the useful question is not only do we have a page in the footer.
The useful question is whether the statement actually matches the way the site collects, explains, shares, stores, and reuses personal information.
That gap matters because the official rules still push toward live accuracy, not decorative legal copy. The California Privacy Protection Agency’s current regulations, effective January 1, 2026, say the purpose of the privacy policy is to provide consumers with a “comprehensive description” of a business’s online and offline information practices, to explain their rights, and to provide the information needed to exercise those rights. GDPR Article 12 still requires information to be presented using “clear and plain language,” while Article 13 still expects the notice to cover items such as purposes, legal basis, recipients, transfers where relevant, and rights. California’s Department of Justice also still tells consumers that a business’s privacy policy should be “updated at least once a year.” And on April 29, 2026, the UK’s ICO finalized guidance that applies not just to classic cookies, but to tracking pixels, device fingerprinting, and similar “storage and access technologies.”
If you want the nearby context first, start with our guides to privacy statement template, privacy policy for website, and website privacy policy template. This page stays narrower. It is the privacy statement for website review I would use this week before publishing or refreshing the live page.
If your team needs help aligning the published statement with the real stack behind it, DataShyre can help through data mapping, consent management, and DSR automation. The risky part is rarely writing the page. The risky part is making sure the page stays true after new forms, tags, vendors, and workflows go live.
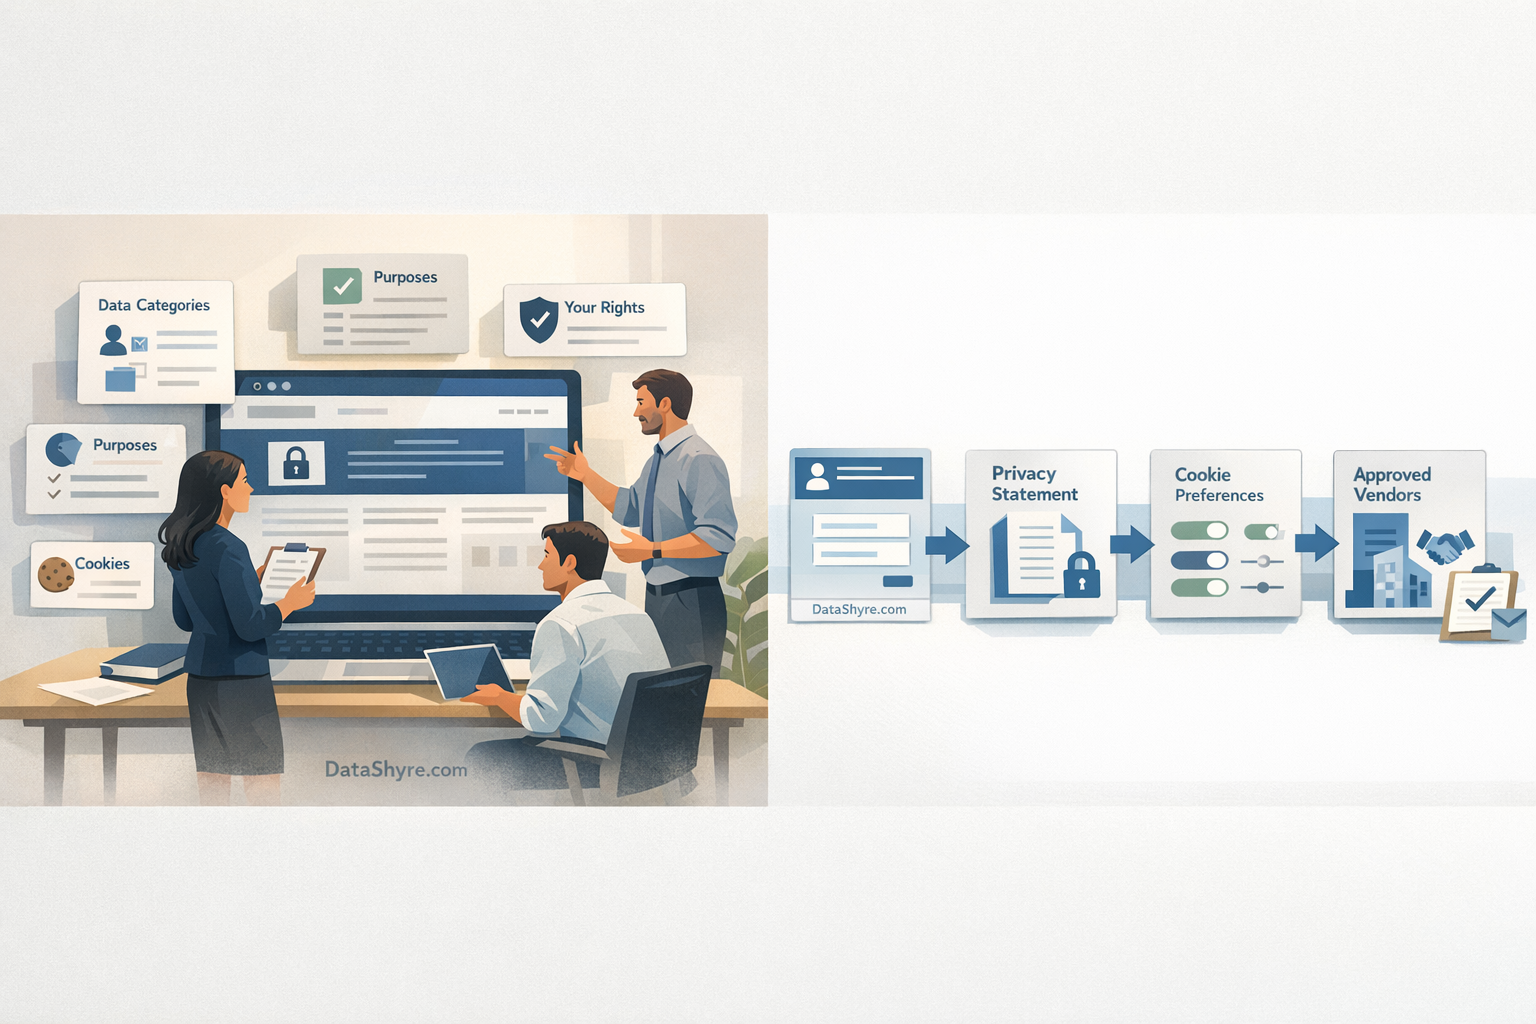
1. Treat the privacy statement as a live disclosure system, not a footer artifact
The first privacy statement for website mistake is acting like the statement is a standalone page that legal owns and nobody else touches.
In practice, it is part of a disclosure system that includes:
- the full privacy statement page;
- webforms and lead-capture pages;
- cookie or preference controls;
- app download or landing pages if a mobile app is involved; and
- account settings or request workflows that users rely on later.
If those parts disagree, the footer page does not save you.
That is why the right first step is not copy editing. It is mapping the live collection points and the systems connected to them.
2. Cover the content blocks the current rules actually call for
A weak privacy statement for website usually sounds polished and still leaves out the most important facts.
The CPPA’s current regulations say the policy should describe online and offline information practices and include a meaningful description of:
- the categories of personal information collected;
- the categories of sources;
- the specific business or commercial purposes;
- the categories of personal information sold or shared, if any;
- the categories of third parties receiving it;
- the retention period or the criteria used to decide it;
- the consumer rights and how to exercise them;
- a contact for privacy questions or concerns; and
- the date the privacy policy was last updated.
GDPR-facing teams usually need the same practical discipline plus the GDPR-specific pieces around lawful basis, recipients, transfers where relevant, and rights.
So before publishing any privacy statement for website page, ask a blunt question: could a normal person read it and understand what you collect, why you collect it, where it goes, how long it stays, and what they can do next?
If the answer is no, the page is not ready.
3. Put the notice where collection happens, not only on the policy page
This is where many decent-looking privacy statement for website projects fail.
The current California regulations say Notice at Collection must be made available at or before the point of collection. They also say that when a business collects information through a webform, it may place a conspicuous link in close proximity to the fields or near the submit button. If the business does not provide the Notice at Collection at or before that moment, the regulations say it shall not collect the personal information.
That matters because a privacy statement page is not a substitute for point-of-collection context.
For privacy statement for website work, that means checking whether:
- signup, contact, demo, and download forms point users to the right notice;
- the link lands on the relevant section rather than a long wall of unrelated text;
- the same logic works on mobile layouts;
- app download or landing pages expose the statement clearly when an app is involved; and
- the full statement and the short notice do not contradict each other.
If people only learn what is happening after they already submitted the form, the disclosure arrived too late.
4. Give cookies, pixels, and similar tracking their own honest explanation
Many weak privacy statement for website pages still bury tracking inside vague phrases like usage data, service improvement, or trusted partners.
That wording is usually too thin for a live site.
The ICO’s finalized 2026 guidance is useful here because it deliberately talks about “storage and access technologies” and says the scope covers cookies, tracking pixels, device fingerprinting, and similar technologies. That is a more honest model for what modern sites actually do.
So your privacy statement for website should explain, in plain language:
- what tracking or storage technologies are used;
- whether they are necessary, analytics, advertising, personalization, or support related;
- whether another party receives data through them;
- how consent or opt-out controls affect them; and
- where the person can revisit those choices later.
The goal is not to dump a scanner report into the page.
The goal is to make sure the statement does not describe a form-only business when the actual site is also running tags, pixels, embeds, and cross-service tracking.
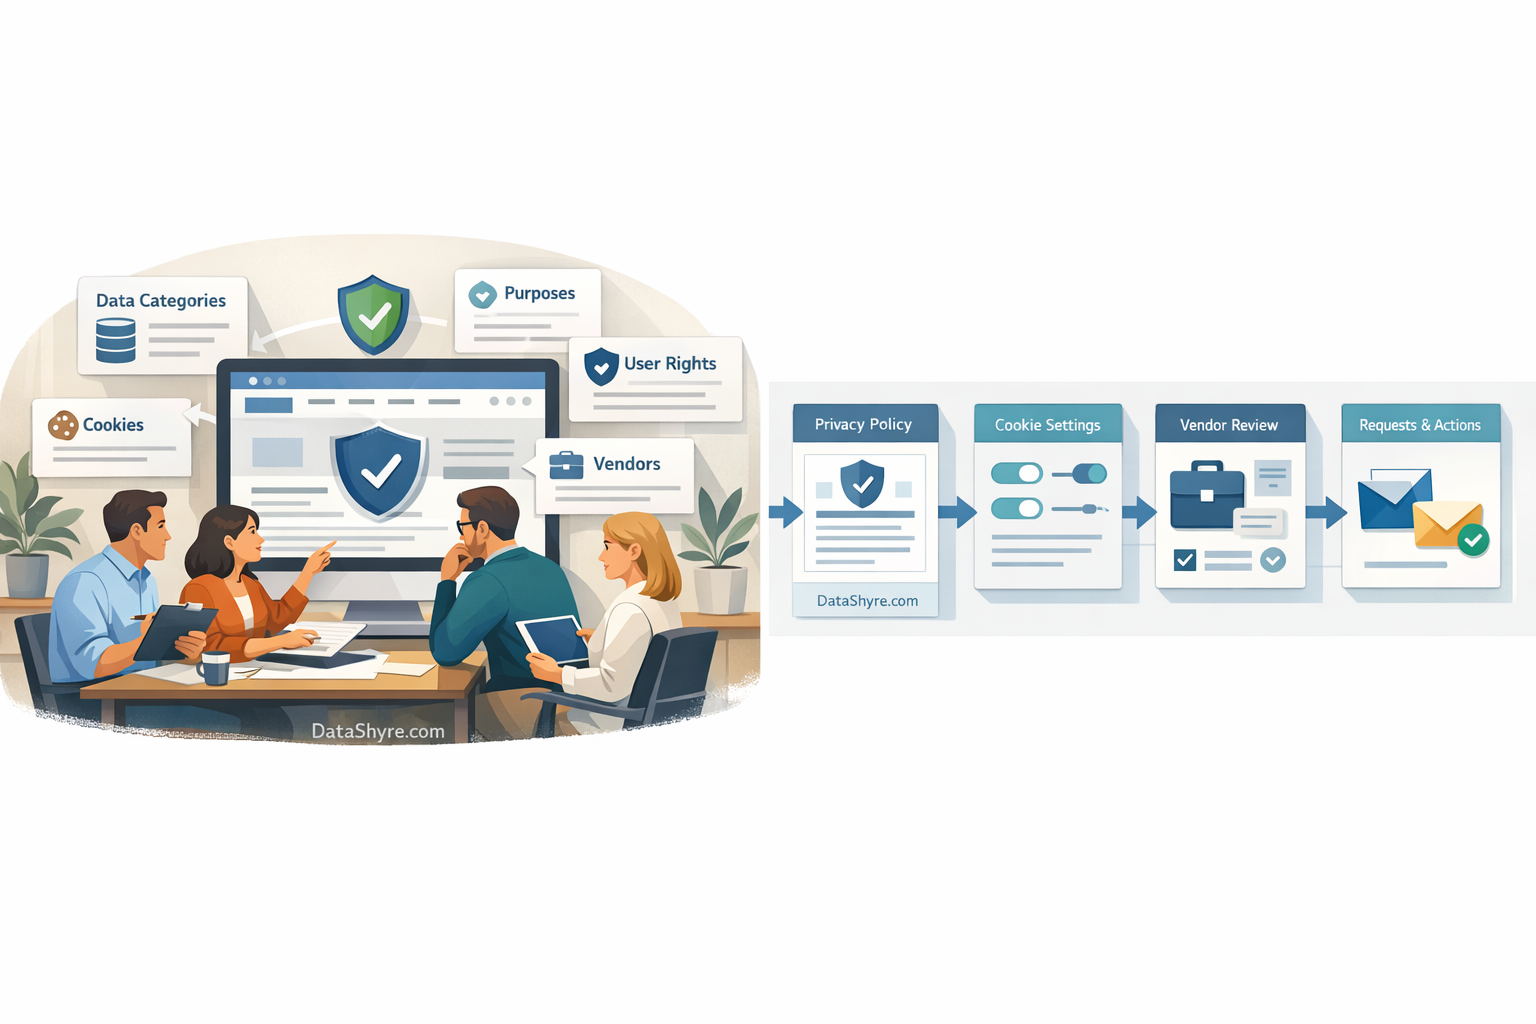
5. Make the rights section operational instead of decorative
Another common privacy statement for website failure is listing rights without making them usable.
The current California regulations say the policy should inform consumers about the rights they have and provide the information necessary to exercise them. That means a page should not stop at naming rights. It should help people act on them.
A practical rights section should tell the user:
- which requests or controls are available in the relevant jurisdiction;
- how to submit a request;
- where to find privacy choices or consent settings;
- whether the business honors opt-out preference signals where applicable;
- what identity verification or follow-up to expect; and
- how to contact someone when the automated path fails.
If the privacy statement says users have control but the page does not show the route to use that control, the statement is not doing its job.
6. Reconcile the statement with the actual vendor and sharing chain
A risky privacy statement for website is often inaccurate because the page lagged behind the stack.
Marketing added a new scheduler. Sales added a form enrichment step. Product added an analytics or session-replay tool. Engineering added a customer-support widget. Nobody came back to the statement.
That is how public language drifts away from reality.
For a serious privacy statement for website review, compare the page against:
- the live form fields and hidden metadata collected;
- the analytics, advertising, chat, booking, and support vendors actually on the site;
- the categories of third parties that receive the data;
- the retention logic used in the systems behind the form; and
- the specific opt-out or consent routes users are promised.
This is also where outside help can save time. DataShyre can audit the live collection path, the downstream vendor map, and the rights workflow so the public statement describes the real system instead of an outdated one.
7. Update the page when the product changes, not only once a year
California’s Department of Justice says the privacy policy should be “updated at least once a year.”
That is a minimum, not a real operating model.
For most teams, the better trigger is change:
- a new form or field goes live;
- a new pixel, tag, SDK, or embed is added;
- a new recipient or processor starts receiving data;
- retention logic changes;
- a new privacy choice or rights path is introduced; or
- the business starts using the data for a new purpose.
That change-based model is how a privacy statement for website stays believable in 2026.
If the page only updates once a year while the marketing stack changes every month, the statement is almost guaranteed to become stale.
A practical review order for this week
If I were approving a privacy statement for website page today, I would use this order:
- map the live collection points, tracking, and downstream vendors;
- fill the required sections for categories, sources, purposes, recipients, retention, rights, contact, and last updated date;
- check the Notice at Collection path on every form or page that gathers personal information;
- review the cookies, pixels, and preference-control section against the real runtime;
- test the request and privacy-choice flows the page promises;
- compare the page against the actual systems and recipients in use; and
- tie future stack changes to a required policy review.
That sequence usually exposes more truth than another pass on tone or formatting.
FAQ
Is a privacy statement for website the same thing as a privacy policy?
Often teams use the terms interchangeably. The important issue is not the label. It is whether the page and connected notices accurately describe collection, use, sharing, rights, and controls.
Does a footer link solve the notice problem by itself?
No. For collection points such as webforms, the current California regulations still expect notice at or before collection, and they specifically contemplate a conspicuous link close to the fields or submit button.
Do I need to mention cookies and similar tracking in the statement?
Usually yes if the site uses them. The exact level of detail can vary, but the statement should honestly explain the tracking and storage technologies in use, the categories or purposes involved, and how people control them.
Bottom line
The best privacy statement for website in 2026 is not the one with the most formal wording.
It is the one that accurately matches the live site.
If your page clearly explains what you collect, why, where it goes, how long it stays, how users exercise their choices, and how cookies or similar tracking really work on the site, you have something useful.
If it is only a footer artifact that lags behind the forms, vendors, and runtime behavior, you have a risk document, not a trust document.
Sources
- California Privacy Protection Agency, CCPA Regulations Effective January 1, 2026: https://cppa.ca.gov/regulations/pdf/ccpa_statute_eff_20260101.pdf
- California Department of Justice, How to Read a Privacy Policy: https://oag.ca.gov/privacy/facts/online-privacy/privacy-policy
- EUR-Lex, Regulation (EU) 2016/679 (GDPR), Articles 12 and 13: https://eur-lex.europa.eu/eli/reg/2016/679/
- ICO, Final storage and access technologies guidance published (April 29, 2026): https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/