Cookie Banner in 2026: 7 Live Checks Before You Call It Compliant
The real value in cookie banner shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for cookie banner is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
A real cookie banner review in 2026 has to cover the visible choice pattern, the actual tags and scripts firing underneath it, the wording on the screen, the records behind the decision, and the operating habits that keep the whole thing true after the next release.
The live regulator picture is useful here. The ICO’s finalized April 29, 2026 storage-and-access guidance says PECR is not only about classic cookies. It also reaches pixels, fingerprinting, web storage, and “scripts and tags.” Its companion compliance guidance is just as direct that you “must not pre-enable non-exempt storage and access technologies” and that consent is required before they run unless an exception applies. On the design side, CNIL’s December 12, 2024 notice on misleading banners says “rejecting cookies should be just as easy as accepting them.” And the broader transparency rule still matters too: GDPR Article 12 requires information in “clear and plain language.”
There is some progress. When the ICO announced its final guidance on April 29, 2026, it also said “99% of the UK’s top 1,000 websites now meet compliance standards for cookie banners.” That is encouraging, but it does not mean your own setup is safe by default. It mostly means the compliance bar is now clearer and easier to compare against.
If you want nearby context first, start with these guides to cookie policy, this website uses cookies, and find tracking cookies. This page stays focused on the cookie banner itself: what it has to show, what the site has to do behind it, and what I would test this week before calling it compliant.
If your team is trying to get cookie banner under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team wants help turning a banner into an actual consent operating system, DataShyre can help with consent management, website privacy testing, and data mapping. The hard part is rarely getting a banner live. The hard part is making the banner, the tag layer, and the policy text tell the same truth.
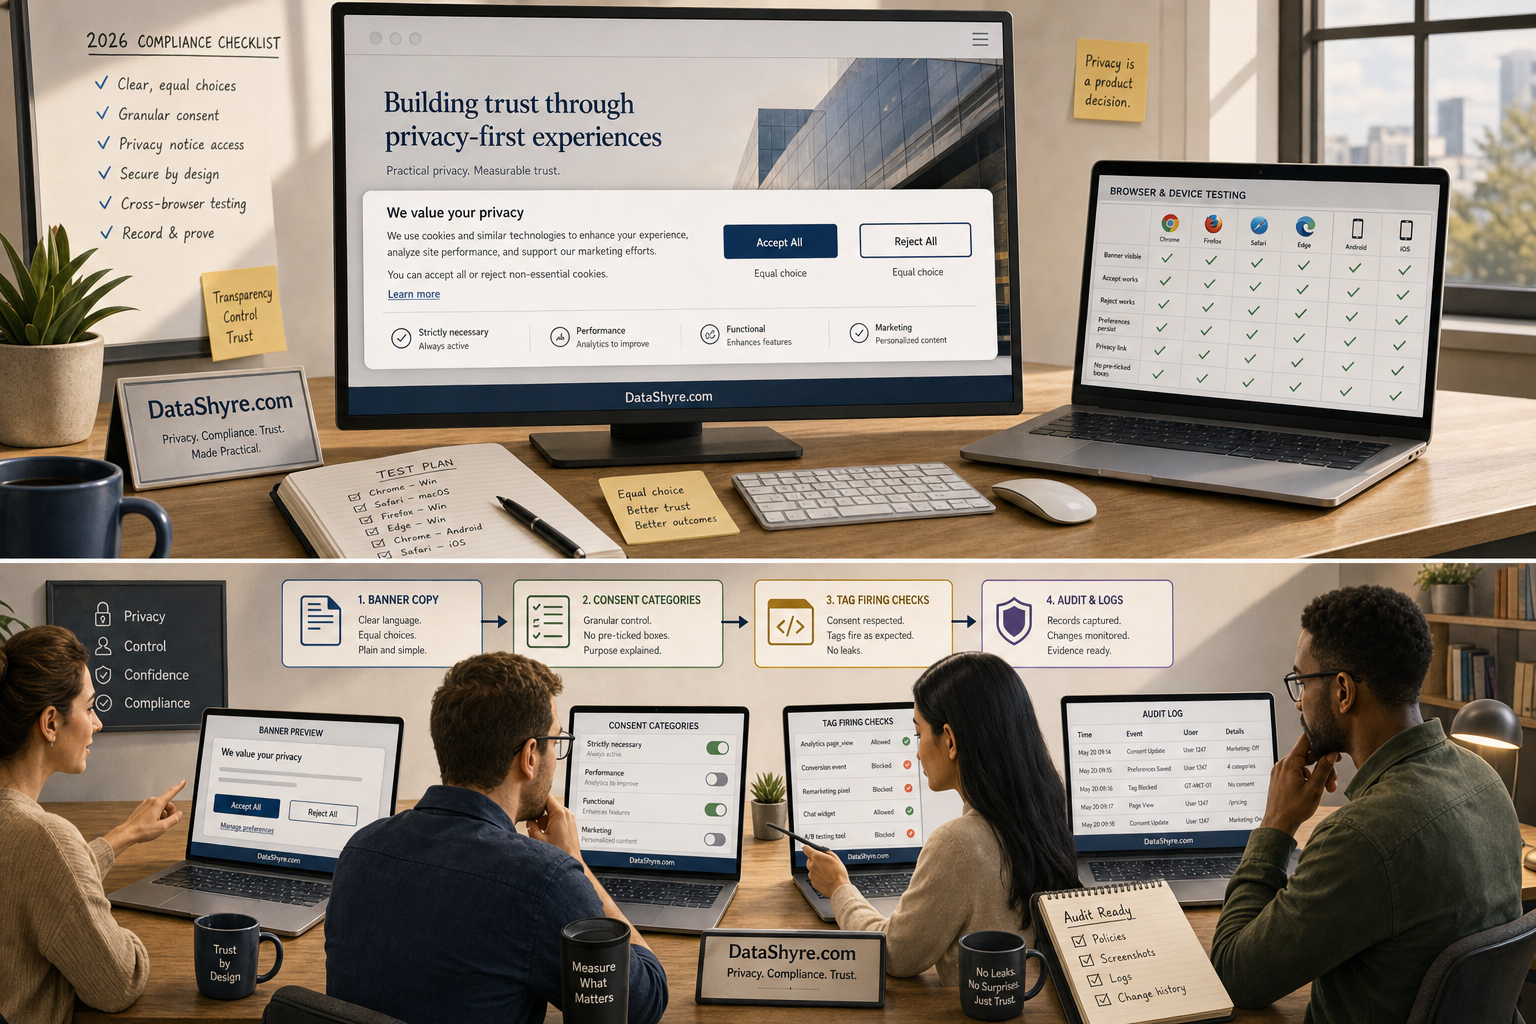
1. Test whether reject is really as easy as accept
This is still the fastest credibility test for a cookie banner.
CNIL’s late-2024 enforcement notice is practical because it names the exact patterns that keep appearing:
- the reject option is a weak text link while accept gets the real button;
- the reject path is buried inside longer explanatory copy;
- the banner repeats the accept path more than once;
- the design nudges the visitor toward yes with color, spacing, or hierarchy.
That means you should test the first layer exactly as a user sees it:
- Is there an explicit reject path on the first layer when consent is required?
- Does reject take the same number of clicks as accept?
- Is reject visually comparable in size, contrast, and placement?
- Can someone understand the choice without opening a policy page first?
If the banner wins consent by friction, it is not a strong cookie banner no matter how polished it looks.
2. Verify what fires before the visitor chooses
This is where many cookie banner implementations fail.
The banner looks calm and balanced.
Meanwhile, analytics, ad, or social tags have already run.
The ICO’s current storage-and-access guidance makes the runtime point clearly: PECR reaches cookies, but it also reaches pixels, web storage, fingerprinting, and “scripts and tags.” Its compliance guidance adds the operational rule that you “must not pre-enable non-exempt storage and access technologies.”
So the real test is not the screenshot.
It is the network and storage behavior:
- what loads before any choice;
- what cookies or local storage entries appear on load;
- what still fires after reject;
- what changes after accept or granular choices;
- whether embedded tools or tag-manager routes bypass the banner logic.
A cookie banner is only defensible when the site behavior matches the promise on screen.
3. Separate exempt functions from everything that still needs consent
One reason cookie banner work gets messy is that teams treat every cookie as if it belongs in the same legal bucket.
It does not.
The ICO’s 2026 guidance keeps the exception analysis purpose-specific. If a technology is strictly necessary for the service a person actually requested, or if it fits the narrow statistical-purpose path on the ICO’s terms, the banner logic may differ. But cross-site tracking, advertising uses, many social plugins, and anything doing broader profiling still need consent.
That means the banner review should map each item by purpose, not by vendor label:
- security or session continuity;
- shopping-cart or explicit service functionality;
- aggregate service-improvement analytics;
- personalization or profiling;
- advertising, retargeting, affiliate, or social tracking.
If your categorization is fuzzy, your cookie banner text will usually be fuzzy too.
4. Rewrite the wording until a normal person can understand it
A lot of cookie banner copy is still written like a legal shrug.
It says cookies are used to improve experience or for analytics and marketing partners without explaining what actually happens.
That is weaker than it sounds. GDPR Article 12 still sets the transparency baseline for related personal-data information: “clear and plain language.” The ICO’s consent guidance also says users need clear and comprehensive information so they understand what you want consent for and what choices they have.
So read the banner copy like a visitor, not like the team that wrote it:
- Does each category name mean anything to a non-specialist?
- Are ad-tech, social, or measurement purposes described in plain English?
- Is the withdrawal path obvious before the user accepts?
- Does the text line up with the policy page and preference center?
If the visitor cannot tell what changes when they click accept, your cookie banner is still too vague.
5. Make the banner easy to revisit after the first choice
Consent is not a one-time magic moment.
It has to stay manageable after the first visit.
The ICO’s consent guidance points to records, fresh consent for new purposes, and user withdrawal as ongoing duties, not launch-day chores. CNIL’s notice also frames banner design around valid consent, which implies a user must be able to do more than just accept once and disappear into the site forever.
For a serious cookie banner setup, test:
- whether the visitor can reopen preferences from every key page;
- whether withdrawal is as practical as the original grant;
- whether category changes actually update tag behavior quickly;
- whether the preference record keeps enough detail to explain what happened later.
If the banner disappears after the first click and the only way back is a hidden footer riddle, the control is weaker than it looks.
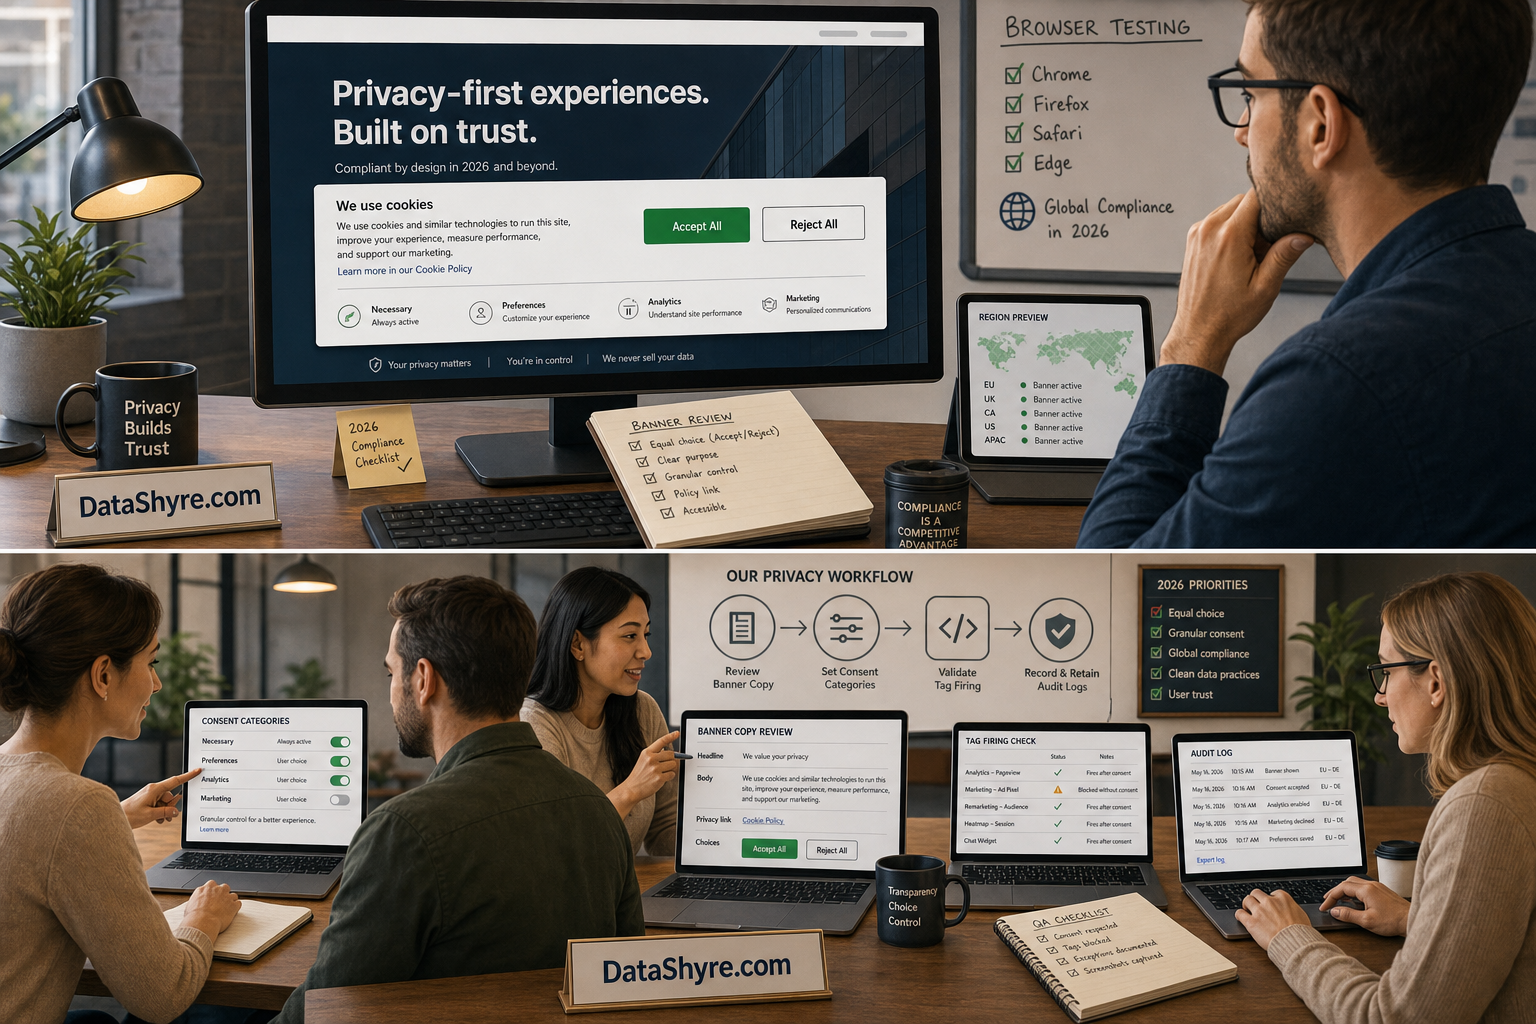
6. Check what happens when the site changes
This is one of the most common cookie banner blind spots.
The launch looked fine.
Then someone added a new tag, a new embedded video, a new CRM form, or a new ad pixel six weeks later.
The ICO’s 2026 consent guidance is explicit that if you introduce new technologies for a different purpose than what you originally stated, you must obtain fresh consent for the new technology or purpose.
So a working cookie banner process should connect privacy review to:
- tag-manager changes;
- plugin installs and app installs;
- new embedded services;
- new analytics or attribution tools;
- changes in category definitions or vendor lists.
If your release process can change tracking without forcing a consent review, the banner will drift out of date faster than the team expects.
7. Treat records and ownership as part of the banner, not a separate project
Many teams talk about the cookie banner as if it ends at the front end.
It does not.
Someone has to own the categorization, the wording, the testing, the vendor inventory, and the evidence trail. The ICO’s current guidance talks directly about keeping records of preferences and considering roles when a CMP provider is involved. That is a reminder that the banner is part of an operating model, not just a component.
A stronger cookie banner program can answer:
- who approves category definitions;
- who tests pre-consent and post-reject behavior;
- who updates the policy when vendors or purposes change;
- where preference evidence lives;
- who signs off before a new tag or partner goes live.
If no one owns those answers, the cookie banner is usually just a nicer-looking risk surface.
A practical cookie banner review for this week
If I were auditing a live cookie banner today, I would use this order:
- compare the first-layer accept and reject experience;
- inspect what cookies, storage, pixels, and tags fire before any choice;
- classify each item by purpose and exception status;
- rewrite the wording until the categories are plain and specific;
- test withdrawal and the ability to reopen choices;
- tie new tags and embeds to a fresh-consent review;
- confirm who owns the records, vendor map, and release approval.
That sequence usually exposes more real risk than endlessly debating colors or button corners.
FAQ
Does every cookie banner need a reject button on the first layer?
Where consent is required, the safest operating position is to make rejection as easy as acceptance. CNIL’s current enforcement notice is explicit on that point, and hiding refusal behind extra friction is still one of the clearest ways to weaken consent.
Is a cookie banner enough if my tag manager is set up correctly?
No. The visible cookie banner and the underlying tag behavior both matter. A balanced-looking banner with pre-firing tags is still a compliance problem.
Can analytics be exempt from consent?
Sometimes, but only in narrow circumstances. The ICO’s 2026 guidance treats the statistical-purposes path as specific and limited. Once the setup goes beyond aggregate service improvement into profiling, advertising, cross-site tracking, or similar uses, consent is generally back on the table.
Bottom line
A cookie banner in 2026 is not a decorative pop-up.
It is the visible edge of a deeper consent system.
You need equal choices, honest wording, runtime behavior that obeys those choices, category logic that reflects real purposes, a practical path to revisit consent later, and release controls that stop new tracking from sneaking past the banner.
The fastest way to judge cookie banner is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- ICO, Final storage and access technologies guidance published (April 29, 2026): https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- ICO, What are storage and access technologies?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/what-are-storage-and-access-technologies/
- ICO, How do we comply with the PECR rules?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/how-do-we-comply-with-the-pecr-rules/
- ICO, How do we manage consent in practice?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/how-do-we-manage-consent-in-practice/
- ICO, What are the exceptions?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/what-are-the-exceptions/
- CNIL, Dark Patterns in Cookie Banners: CNIL issues formal notice to website publishers (December 12, 2024): https://www.cnil.fr/en/dark-patterns-cookie-banners-cnil-issues-formal-notice-website-publishers
- European Data Protection Board, Report of the work undertaken by the Cookie Banner Taskforce (January 18, 2023): https://www.edpb.europa.eu/documents/task-force-report/report-of-the-work-undertaken-by-the-cookie-banner-taskforce_en
- EUR-Lex, Regulation (EU) 2016/679, Article 12: https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:32016R0679