Best Privacy Policy Generator in 2026: 7 Checks Before You Trust One
The real value in best privacy policy generator shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for best privacy policy generator is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
The best generator is not the one that sounds the most legal. It is the one your team can turn into a page that still matches the live website, app, forms, cookies, embedded tools, vendors, and rights workflow after the next release.
The official sources still point in that direction. California’s Department of Justice says a notice at collection must link to the privacy policy so people can get a “fuller description” of privacy practices and rights. The CPPA’s current notice guidance says a business must post and maintain the privacy policy through a link using the word “privacy.” GDPR Article 12 still requires privacy information to be presented in a concise, transparent, and easily accessible form using “clear and plain language.” The ICO still says to “know what personal data you have” before drafting privacy information. And WordPress still says it is your responsibility to keep the final policy “current and accurate.”
If you want nearby context first, start with these guides to privacy policy template, website privacy policy generator, and privacy policy creator. This page stays narrower. It is the best privacy policy generator review I would use this week before trusting any product to draft a live privacy page.
If your team is trying to get best privacy policy generator under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team is comparing generators because the privacy page has already drifted away from the live stack, DataShyre can help. Our work around data mapping, consent management, and DSR automation is aimed at exactly that gap between the draft and the runtime reality.
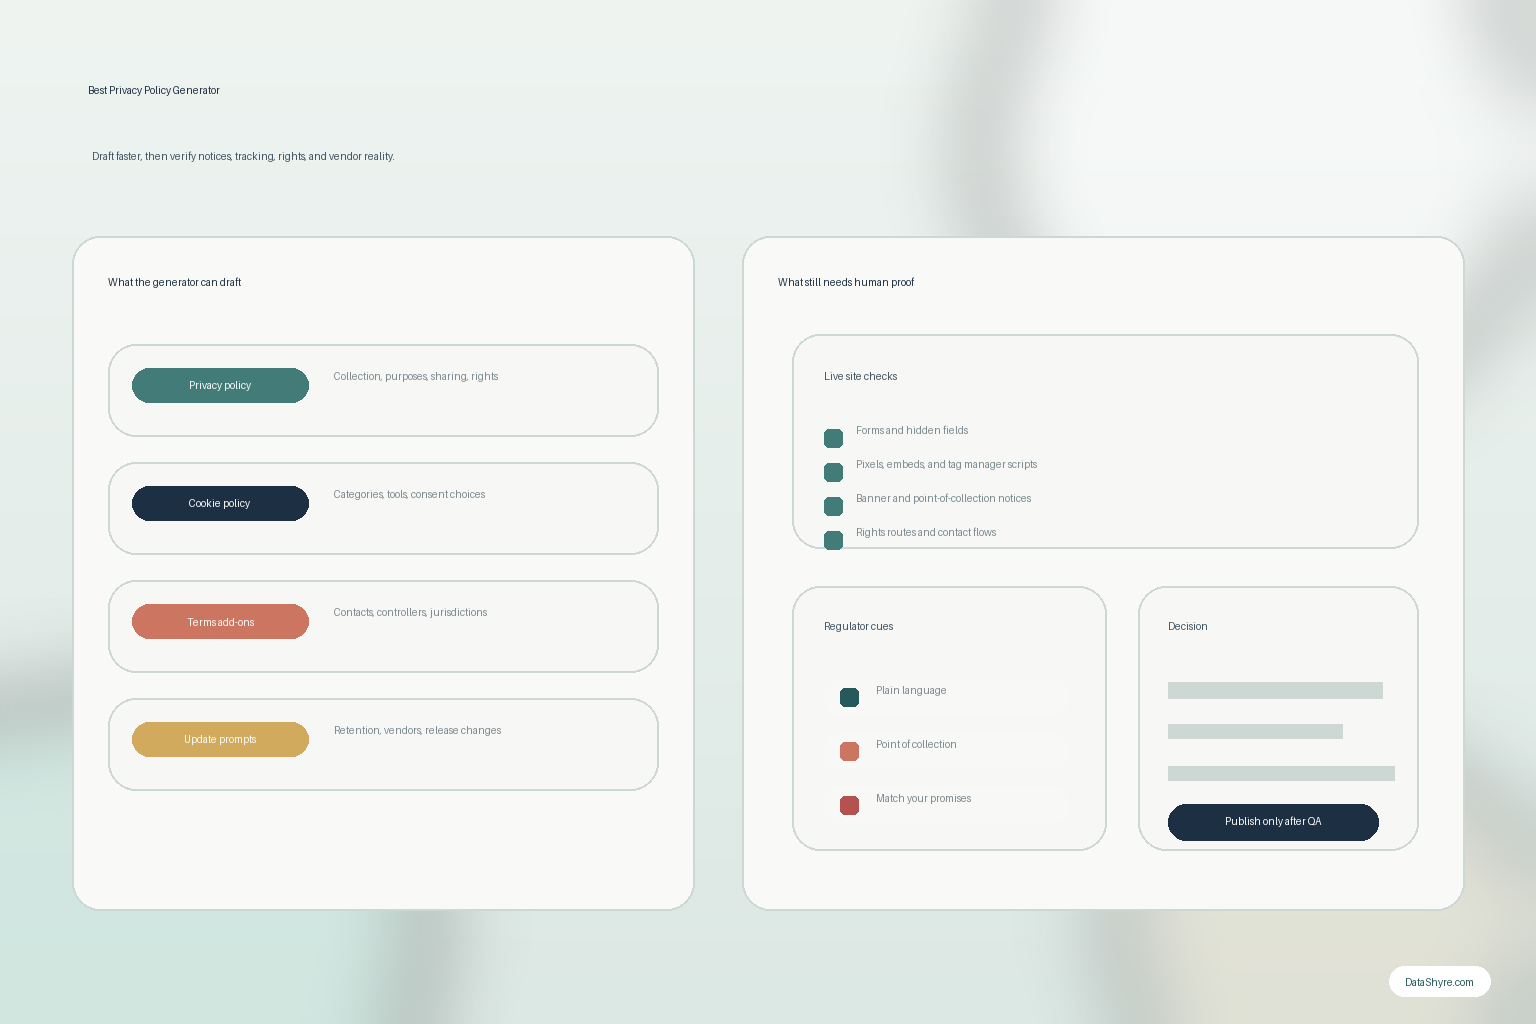
1. Buy for disclosure coverage, not for the prettiest draft
The first best privacy policy generator mistake is confusing polished wording with complete disclosure.
A generator can sound careful while still leaving out the sections regulators expect users to understand.
For a real comparison, start with the blocks your final page still has to cover:
- who operates the service and how to contact them;
- what categories of personal data are collected;
- where the data comes from;
- why the data is used;
- who receives it or what categories of recipients receive it;
- how long it is retained or how retention is decided; and
- what rights people have and how to exercise them.
This is why the best privacy policy generator is rarely the one with the fewest questions. It is usually the one that forces the right questions early enough for the answers to stay specific.
2. Check whether the generator supports the collection moment, not only the footer page
This is where many privacy tools become too decorative.
California’s current CCPA guidance still treats the notice at collection and the policy page as connected. The notice has to appear at or before collection and link to the policy for the fuller explanation. That means a generator should help you think beyond the final page.
When comparing a best privacy policy generator workflow, ask whether it helps your team align the policy with:
- contact and demo forms;
- newsletter and marketing signups;
- checkout, booking, or registration flows;
- app onboarding screens;
- cookie and preference-entry points; and
- account settings or request forms.
If the tool only helps you publish a footer page, it may still leave the live collection experience underspecified.
3. Treat cookies, trackers, and embeds as a separate evaluation branch
This is one of the easiest ways to overrate a generator.
Many tools can draft a competent-looking privacy page while flattening cookies, pixels, embedded video, chat widgets, analytics tags, and third-party scripts into vague phrases like usage data or trusted partners.
That is not enough for a serious best privacy policy generator review.
The better question is whether the tool can support a clean explanation of:
- what cookies or similar technologies are in use;
- which of them are necessary versus analytics, advertising, personalization, or support-related;
- which third parties may receive data through them;
- how consent or opt-out choices affect them; and
- where the user can revisit those choices later.
If this is the part of your stack that keeps drifting, pair this page with these guides to generate privacy policy and privacy policy example for website. They stay closer to what the final page should actually communicate.
4. Prefer generators that make human review easy instead of hiding the assumptions
The best tools do not pretend they know your business better than your team does.
They make it easier to inspect the assumptions and rewrite the weak parts.
The ICO’s current drafting guidance still starts with the same practical rule: “know what personal data you have” before you write the notice. That means the best privacy policy generator should leave room for editing around real forms, vendors, transfers, and retention logic instead of locking you into generic prose.
That matters because the privacy page usually goes stale in the same places:
- a new vendor is added;
- a new form or lead flow launches;
- marketing adds new tags or embeds;
- the product starts reusing data for a new purpose; or
- the rights-handling path changes behind the scenes.
If the generator makes those sections hard to revise or hard to trace back to reality, it is optimizing for speed over trustworthiness.
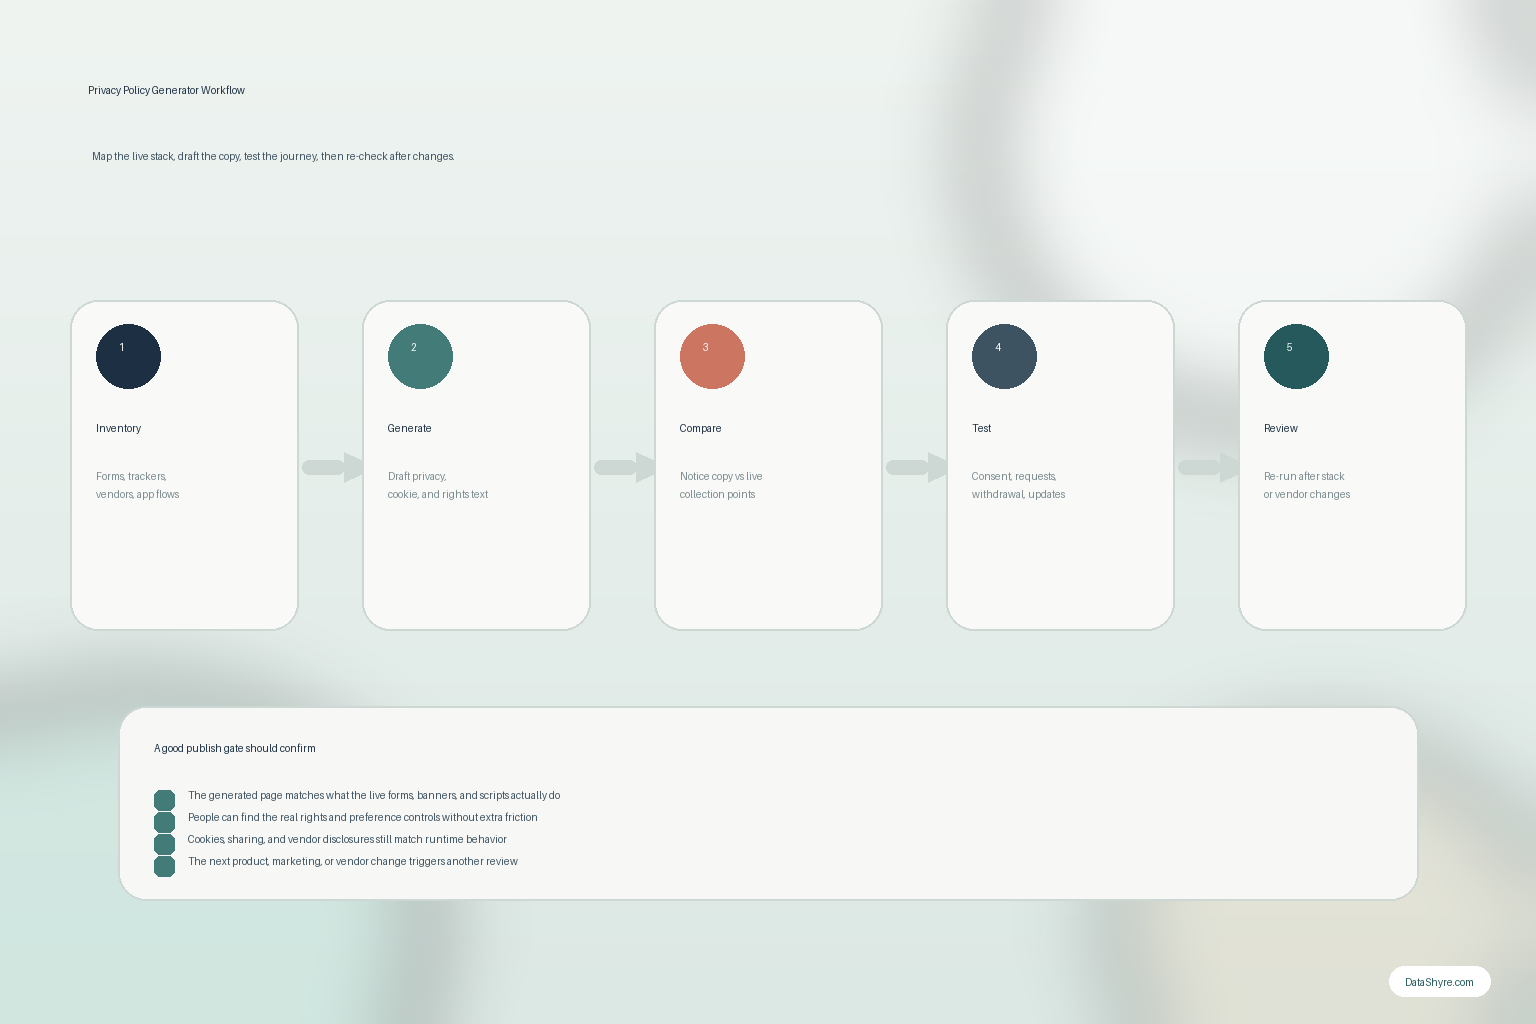
5. If your site runs on WordPress, score the generator against the real plugin stack
This is where a lot of buyers make the wrong comparison.
WordPress already ships privacy tooling, and its developer guidance says plugins that collect, use, store, or pass user data to third parties should add suggested text for the site’s privacy policy. WordPress also says the final policy still has to be kept “current and accurate.”
So for WordPress teams, the best privacy policy generator is not automatically the flashiest external tool.
It is the one that helps you reconcile:
- WordPress starter text;
- participating plugin disclosures;
- custom scripts and embeds;
- cookie-banner behavior;
- forms created by builders or plugins; and
- the live page people actually reach in the footer or settings flow.
If the generator cannot work cleanly with the WordPress stack you already have, the output will look more complete than it really is.
6. Test the rights section like a user, not like a copy editor
This is where the best-looking drafts often fall apart.
California’s current notice guidance still expects the privacy policy to explain rights and how to exercise them. The CPPA’s FAQ also still says businesses subject to the CCPA must post their policy through a link using the word “privacy” on the homepage and other webpages.
So a serious best privacy policy generator review should verify that the final page clearly tells people:
- which rights may apply;
- how to submit a request;
- where to find opt-out or preference controls;
- whether there is an account-based route for existing users;
- how the privacy link is labeled and where it appears; and
- what happens after a request is submitted.
If the generated page names rights without a working route, the tool has not solved the most important part.
7. Choose the generator that survives releases, not the one that demos best
The long-term privacy problem is usually not drafting. It is drift.
California’s current notice guidance says the policy must be maintained, and WordPress says the same thing in plainer product language: keep it “current and accurate.” The ICO’s drafting guidance also says privacy information should be reviewed and updated before personal data is used for a new purpose.
That means the best privacy policy generator is the one your team can realistically revisit when:
- the site adds a new vendor or processor;
- the app launches a new collection flow;
- the banner, preference center, or consent logic changes;
- retention periods or data uses shift;
- the business expands into a new region; or
- support changes how it handles privacy requests.
If the tool makes those refreshes painful, the page will become misleading faster than the initial demo suggested.
A practical 7-step scorecard for this week
If I were comparing best privacy policy generator options today, I would score them in this order:
- disclosure coverage for real legal and operational sections;
- fit with point-of-collection notices and live forms;
- ability to explain cookies, embeds, and trackers honestly;
- ease of human review and revision;
- fit with the site’s CMS and plugin stack;
- clarity of rights and privacy-link deployment; and
- how easy it is to keep the page aligned after release changes.
That scorecard usually tells you more than a polished product demo.
FAQ
Can the best privacy policy generator make my site compliant by itself?
No. It can speed up drafting, but it cannot verify live forms, trackers, vendors, consent behavior, or request handling on its own.
Should the best privacy policy generator also help with cookies?
At minimum it should make room for a truthful cookie and tracking explanation. A separate CMP or cookie tool may still do the runtime enforcement work.
Is WordPress’s built-in privacy helper enough on its own?
Not always. It can be useful starter text, especially when plugins participate, but WordPress is explicit that the final policy still has to be reviewed and kept current by the site owner.
Bottom line
The best privacy policy generator in 2026 is not the one that writes the longest draft.
It is the one your team can verify against live collection points, cookies, vendors, rights paths, and change management without guessing what the site actually does.
If that verification step is weak, the tool is only helping you publish faster.
The fastest way to judge best privacy policy generator is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- California Department of Justice, California Consumer Privacy Act (CCPA): https://oag.ca.gov/privacy/ccpa
- California Privacy Protection Agency, What General Notices Are Required by the CCPA?: https://cppa.ca.gov/pdf/general_notices.pdf
- California Privacy Protection Agency, Frequently Asked Questions (FAQs): https://cppa.ca.gov/faq
- EUR-Lex, Regulation (EU) 2016/679, Article 12 and Article 13: https://eur-lex.europa.eu/eli/reg/2016/679/oj/eng
- ICO, How should we draft our privacy information?: https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/individual-rights/the-right-to-be-informed/how-should-we-draft-our-privacy-information/
- WordPress.org Documentation, WordPress Privacy: https://wordpress.org/documentation/article/wordpress-privacy/
- WordPress.org Documentation, Settings Privacy screen: https://wordpress.org/documentation/article/settings-privacy-screen/
- Developer.WordPress.org, Suggesting text for the site privacy policy: https://developer.wordpress.org/plugins/privacy/suggesting-text-for-the-site-privacy-policy/