Find Tracking Cookies in 2026: 7 Live Checks to See What Your Website Really Loads
The real value in find tracking cookies shows up when you debug it like a live system. A banner can render perfectly and still leak requests, misfire tags, or drift after the next plugin or theme update.
The useful test for find tracking cookies is whether the live stack behaves correctly before consent, after consent, and after the next deployment. That is how hidden leaks and timing mistakes show up.
you find tracking cookies by testing the live website in a clean browser state, comparing what loads before and after user choice, and checking which third parties still receive data.
That broader approach matters because current official guidance no longer treats the issue as classic cookies alone. Chrome’s own developer docs now tell teams where to “identify and inspect third-party cookies” inside DevTools. Firefox says cross-site tracking cookies are “disabled by default” for its users. The California DOJ’s Healthline action said a “consent banner” that looked right still failed because it did not disable tracking cookies. And CNIL’s current guidance still says sites generally have to inform users, “obtain their consent,” and give them a refusal path before dropping or reading non-exempt trackers.
So if you want to find tracking cookies in a way that is actually useful for compliance, product, and vendor review, you need a runtime method instead of a copy-only review.
For adjacent context, start with these guides to tracking cookies, third party cookies, and website privacy checker. This page stays narrower. It is the find tracking cookies workflow I would use this week before trusting what a banner or privacy policy says.
If your team is trying to get find tracking cookies under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team already knows the banner language but still cannot prove what the site actually loads, DataShyre can help with consent management, data mapping, and DSR automation. The hard part is usually not naming categories. It is proving which tools, tags, and third parties still activate across real user journeys.
1. Start with a clean test state before you try to find tracking cookies
The first mistake in any find tracking cookies review is testing a browser that already has old state inside it.
Use a fresh private window or clear site data first.
That matters because saved sessions, previous consent choices, and leftover identifiers can make a site look cleaner or noisier than it really is on first load.
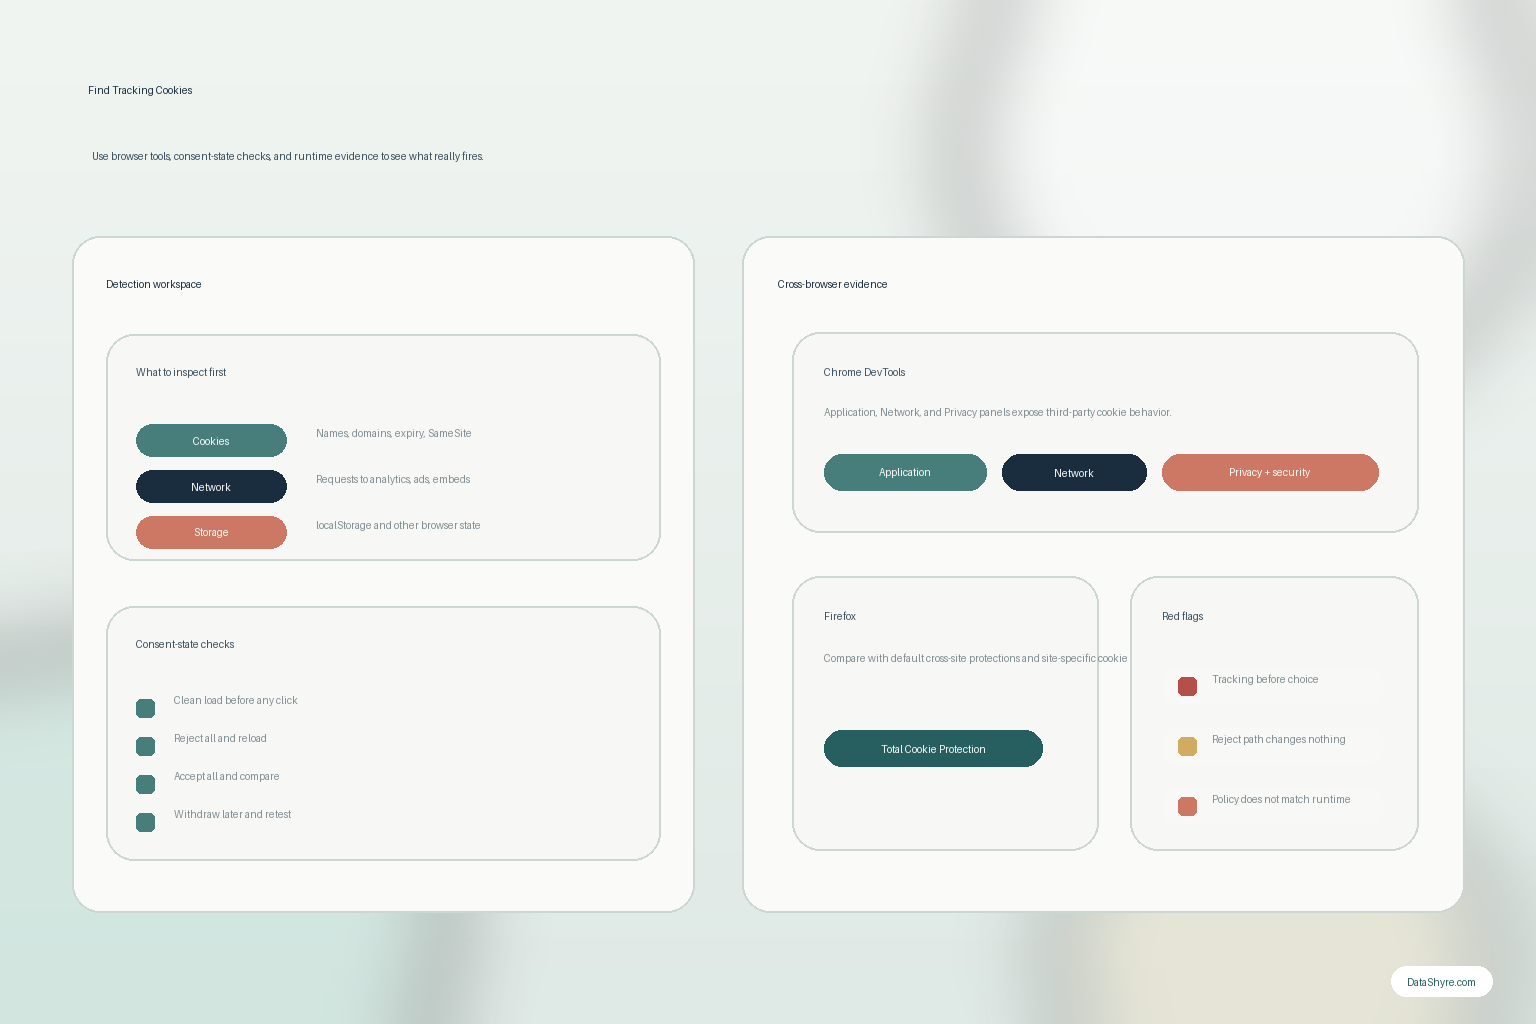
If you want to find tracking cookies accurately, your first pass should answer:
- what appears before any click;
- which domains are setting or reading state;
- whether the site stores only necessary state or also optional tracking state; and
- whether any third-party requests fire before the user chooses anything.
That clean-load snapshot is your baseline.
2. Use Chrome DevTools to inspect cookies and related requests
Chrome’s current developer documentation is still one of the clearest practical sources here.
It says DevTools can “identify and inspect third-party cookies” in Application > Storage > Cookies, and it also says you can find them in Network > request > Cookies.
Chrome’s newer Privacy and security panel adds another useful layer. It lets you temporarily limit third-party cookies while DevTools is open, inspect which ones were allowed or blocked, and see recommendations tied to the affected cookies.
So if you need to find tracking cookies on a live site, Chrome gives you three immediate views:
Applicationto review cookie names, domains, expiry, andSameSite;Networkto see which requests carry cookie-related state; andPrivacy and securityto test how the site behaves when third-party cookies are limited.
That is much more useful than looking at banner copy alone.
3. Cross-check in Firefox because browser defaults already differ
Firefox is useful because its defaults can expose tracking assumptions teams miss in Chromium-only testing.
Mozilla’s current help says third-party cookies, also called cross-site cookies, are cookies set by a different website than the one a person is visiting. It also says cross-site tracking cookies are “disabled by default” for Firefox users, and that Total Cookie Protection keeps cookies inside a site-specific jar.
That means a serious find tracking cookies review should not stop with one browser.
Use Firefox to check:
- whether the site breaks when cross-site tracking cookies are restricted;
- whether embedded tools quietly depend on third-party state;
- whether the consent flow changes anything in practice; and
- whether the same third-party requests appear across browser families.
If a website works only when tracking-friendly assumptions hold, that is already telling you something important.
4. Do not limit the review to cookies alone
This is one of the most common late-2026 mistakes.
The ICO’s April 29, 2026 storage-and-access-technologies guidance says the rules now cover cookies, tracking pixels, device fingerprinting, web storage, and scripts or tags. The EDPB’s Guidelines 2/2023 on the technical scope of Article 5(3) explain that storing or accessing information can also happen when JavaScript or other code instructs the browser or device to send information back over the network.
So the better find tracking cookies question is not only which cookies exist.
It is:
- which identifiers or storage methods are in play;
- which scripts or pixels trigger them;
- which third parties receive the data; and
- whether the site is using a substitute technique that creates nearly the same privacy effect.
This is why the word cookies is only the start of the audit.
5. Compare four live states instead of one
If you want to find tracking cookies in a way that stands up to review, compare these states separately:
- first load before any choice;
- explicit reject all;
- explicit accept all; and
- later withdrawal from the preference center or privacy settings.
This is where weak implementations usually show themselves.
A site may look fine on the accepted path and still fail on the reject or withdrawal path.
California’s DOJ CCPA guidance still says the “notice at collection” must appear at or before collection and must link to the privacy policy for a fuller description of practices and rights. That matters because the collection experience, the banner, and the browser behavior should all line up. In the Healthline case announced on July 1, 2025, the DOJ said the website used a “consent banner” that did not disable tracking cookies even though it claimed to.
That makes the live-state comparison non-optional.
6. Check whether audience measurement or personalization really qualifies for any exemption
A lot of teams assume analytics is automatically safe.
CNIL’s current guidance is more careful than that. It says that, generally, before depositing or reading a cookie or tracer, site operators must inform users, “obtain their consent,” and provide a way to refuse. It also says audience measurement tools only move into an exemption path if specific conditions are met, such as limited purposes, scoped use, objection rights, and technical limits.
CNIL’s enforcement line stayed active in 2026. On October 29, 2026, it announced a 7 million euro fine against FNAC DARTY entities after finding a mobile-app tracker collected browsing history for recommendations and algorithm training without honoring the user’s choice not to consent.
So when you find tracking cookies, do not stop at this looks like analytics.
Check:
- whether the purpose is really limited;
- whether the same data is reused elsewhere;
- whether another party benefits from it;
- whether the user can refuse it; and
- whether the runtime behavior reflects that refusal.
7. Save evidence so you can retest after site changes
The best find tracking cookies workflow is repeatable.
Take screenshots, save request lists, note domains, and record which technologies appeared in each state. That way you can compare the next release against the current one instead of starting from scratch every time.
This matters because tracking changes often come from:
- a tag-manager publish;
- a new plugin or embed;
- a changed vendor configuration;
- a new ad or analytics integration; or
- a redesigned banner or preference center.
If you only test once, you only know one moment.
A practical 7-step workflow to find tracking cookies this week
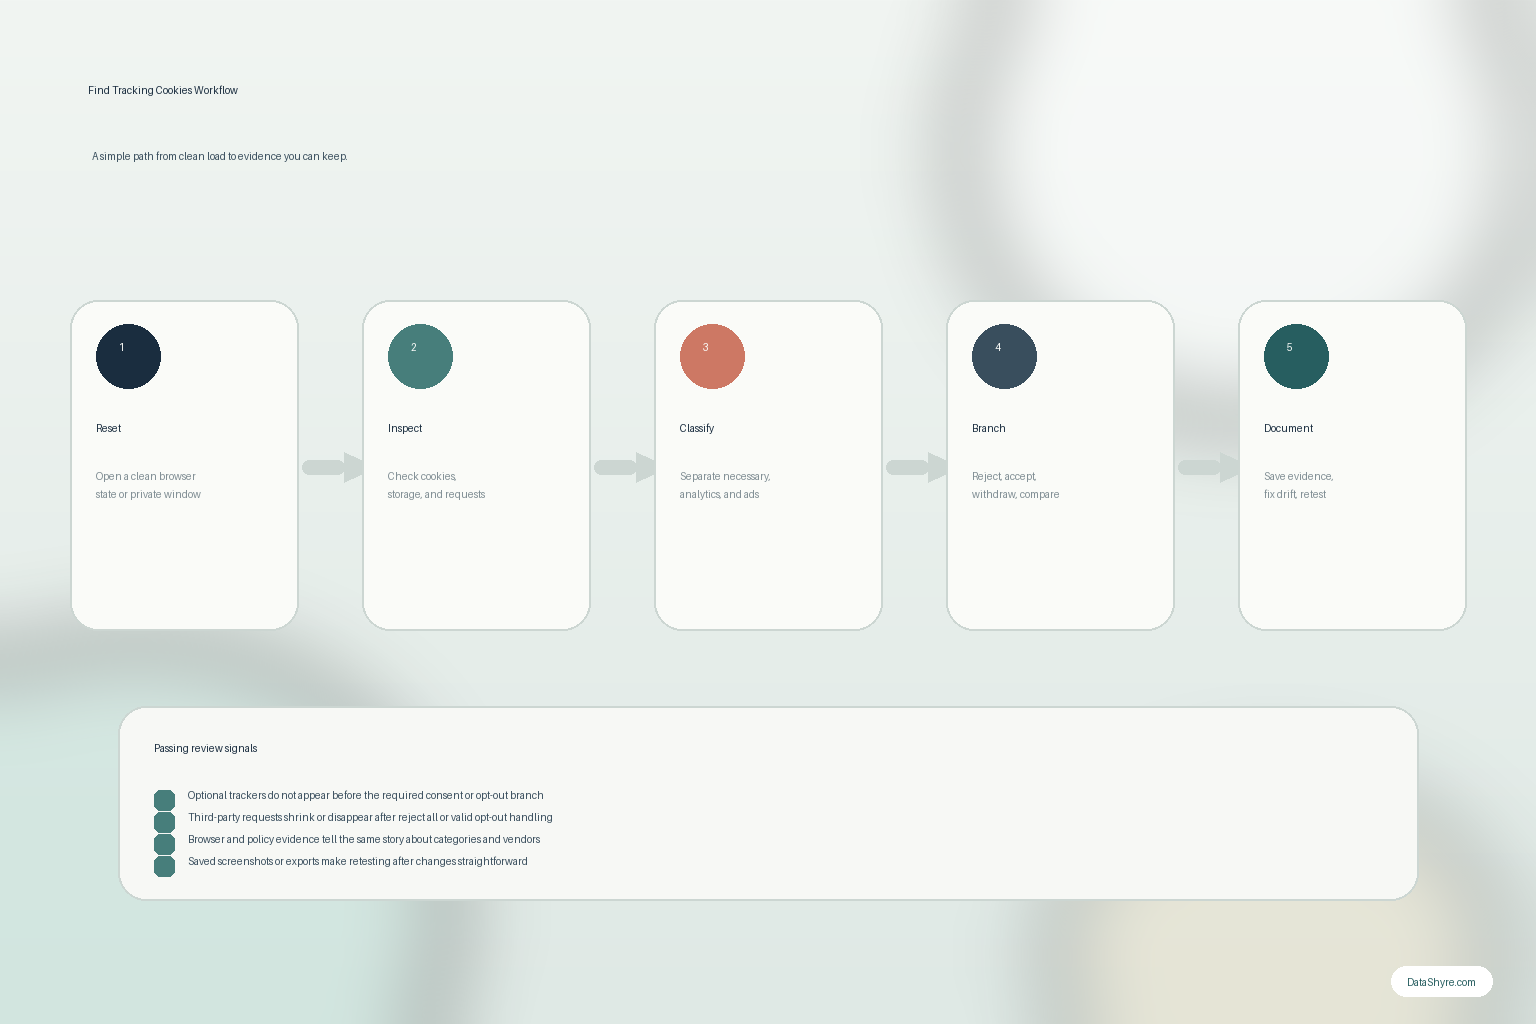
If I needed to find tracking cookies on a live site today, I would use this order:
- open a clean browser state and capture first load;
- inspect
Application,Network, and storage behavior in Chrome DevTools; - cross-check the same page in Firefox;
- list cookies, scripts, pixels, and third-party hosts by purpose;
- compare reject all, accept all, and withdrawal behavior;
- match the runtime result against the banner, notice, and privacy policy; and
- save evidence so the next release can be re-tested fast.
That order catches more real problems than reading the policy first.
FAQ
What is the fastest way to find tracking cookies?
Start with a clean browser session, then inspect Chrome DevTools Application and Network panels before and after consent choices. That usually exposes the main tracking path quickly.
Are tracking cookies always third-party cookies?
No. Some tracking can happen through first-party cookies or through other browser-side technologies. This is why you should inspect requests, storage, and vendor behavior, not only cookie labels.
If I reject cookies and still see third-party requests, is that a problem?
Potentially yes. Some third-party requests may be necessary for the service, but optional analytics, advertising, or personalization flows should not simply survive unchanged where consent or opt-out rules require a real behavior change.
Bottom line
The best way to find tracking cookies in 2026 is to treat the question as a live browser test, not a wording review.
The fastest way to judge find tracking cookies is to test it the way a broken deployment would expose it: before consent, after consent, and again after a stack change.
Sources
- Chrome for Developers, “View, add, edit, and delete cookies”: https://developer.chrome.com/docs/devtools/application/cookies
- Chrome for Developers, “Privacy and security panel”: https://developer.chrome.com/docs/devtools/security
- Mozilla Support, “Third-party cookies and Firefox tracking protection”: https://support.mozilla.org/en-US/kb/third-party-cookies-firefox-tracking-protection
- ICO, “Cookies and similar technologies”: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guide-to-pecr/cookies-and-similar-technologies/
- ICO, “Final storage and access technologies guidance published” (April 29, 2026): https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- California Department of Justice, “California Consumer Privacy Act (CCPA)”: https://www.oag.ca.gov/privacy/ccpa
- California Department of Justice, “Attorney General Bonta Announces Largest CCPA Settlement to Date, Secures $1.55 Million from Healthline.com” (July 1, 2025): https://www.oag.ca.gov/news/press-releases/attorney-general-bonta-announces-largest-ccpa-settlement-date-secures-155
- CNIL, “Sheet n°16: Use analytics on your websites and applications”: https://www.cnil.fr/en/sheet-ndeg16-use-analytics-your-websites-and-applications
- CNIL, “Cookies and mobile application: 7 million euros fine against FNAC DARTY PARTICIPATIONS ET SERVICES and FNAC DIRECT” (October 29, 2026): https://www.cnil.fr/en/sanction-app-cookies-fnac
- European Data Protection Board, “Guidelines 2/2023 on Technical Scope of Art. 5(3) of ePrivacy Directive”: https://www.edpb.europa.eu/documents/guideline/guidelines-22023-on-technical-scope-of-art-53-of-eprivacy-directive_en